
Remember California: no on 44, yes on 40!

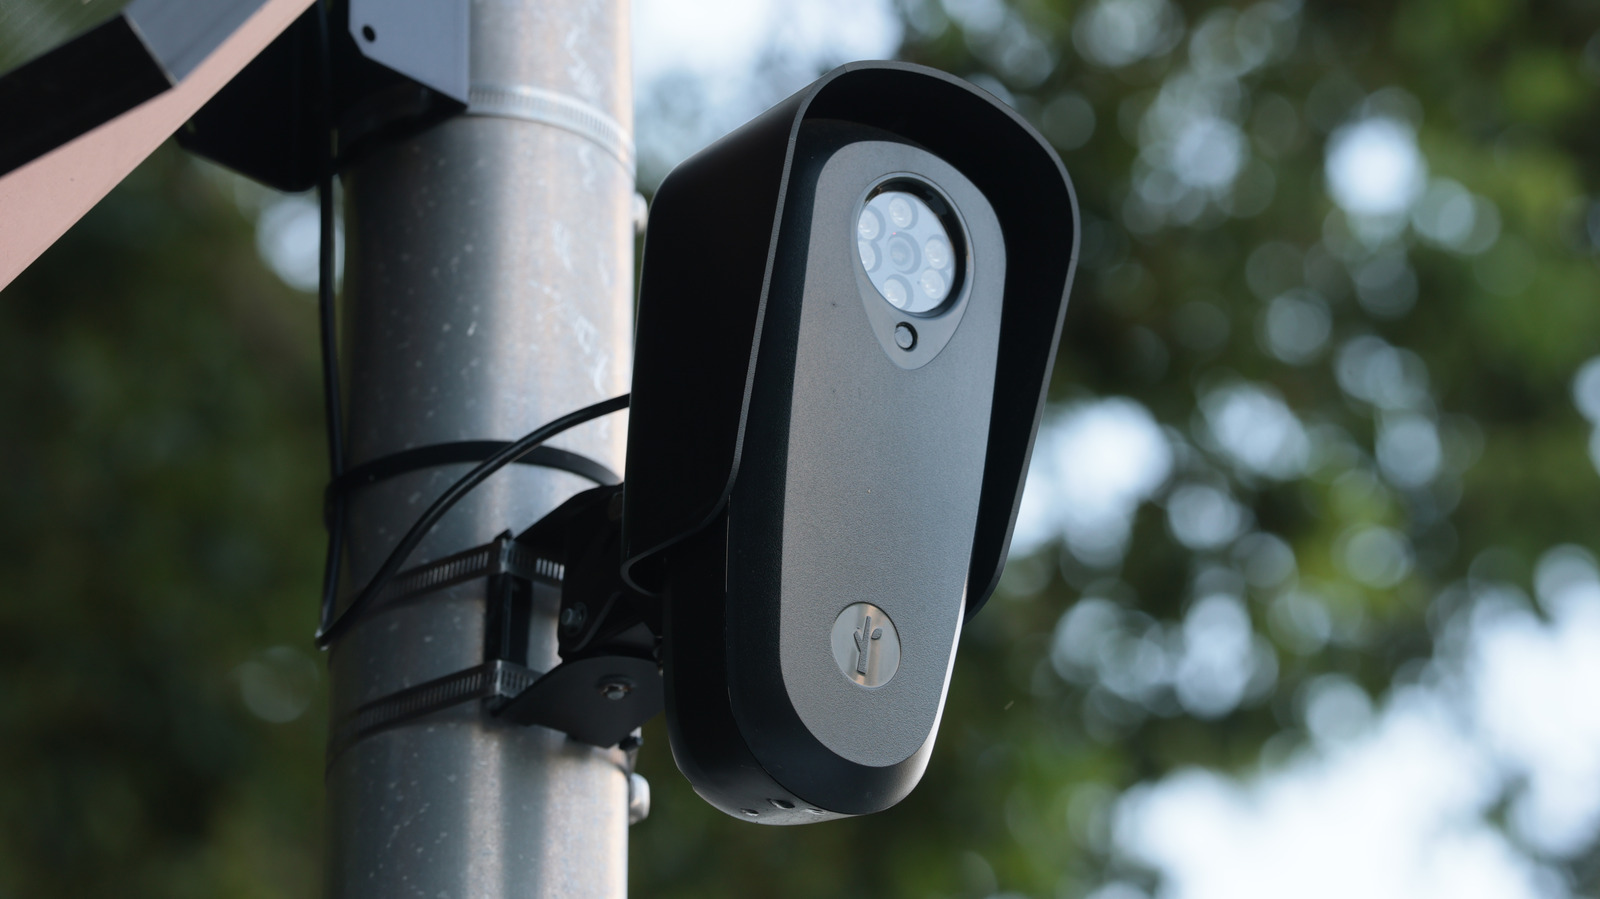


@thenewoil Idly wondering who owns the liabilities here. Best guess is "Nobody, that's just how it is" followed closely by "The town or city, duh."

Maybe he's born with it
Maybe it's Maybelline

@stux Harry the kids always up in everyone's face trying to "Move the needle" and it's f@$kin annoying. nobody can work.
OK, ok I'll give him some bullshit title and pay him to go away.
Felix Hlatky
boosted

3 media files


Why I think attackers can't just keep on getting faster https://en.wikipedia.org/wiki/Lotka%E2%80%93Volterra_equations namely it's not actually worth it and the number of valuable targets isn't infinite.

(checks IT news)
BleepingComputer: Barracuda warns of critical flaws allowing root access to devices
(pre coffee brain queues up soundtrack)
Heart - "Barracuda"
Heart - "Barracuda" (1977)
YouTube

stand a little out of my sun 🍉
boosted

There are many options for ice cream in Beautiful Luxurious Muncie, but it often turns into a gang situation

💬 WARUM gibt es bisher noch keinen jährlichen #Mastodon-Event? 🤔
@Aakerbeere Primär fehlen uns die Ressourcen dafür. @Mastodon


Heads up: A password management app/platform called Msecure from mSeven Software says it recently learned of suspicious activity associated with its app. Here is the important part of their advisory:
"Given the potential security implications, mSeven recommends that you immediately take steps to protect all confidential information stored within the mSecure password management application. This may include changing passwords, resetting or re-enrolling two-factor authentication methods, or removing existing passkeys."
There isn't much else to the notice. I've pasted the entire thing below anyway.
"Important Security Notice
mSeven Software (“mSeven”) recently learned of suspicious activity associated with the mSecure password management application. In response, mSeven quickly launched an investigation, took steps to mitigate the issue, and engaged external cybersecurity experts to assist. You are receiving this email because you are a current or former mSecure customer.
Given the potential security implications, mSeven recommends that you immediately take steps to protect all confidential information stored within the mSecure password management application. This may include changing passwords, resetting or re-enrolling two-factor authentication methods, or removing existing passkeys.
We regret any inconvenience that this may cause.
Sincerely,
The mSeven Software Team"


@briankrebs If you have a limited number of accounts or devices, I can see a way of a digital life being safe without a password manager.
 Posted in
GNU/Linux Italia

Ciao Feditalianз,
cerco un servizio SPID, firma digitale e una PEC che siano gestiti da non-profit, cooperative, o in generale enti che ci piacciono 🌻
In particolare, mi serve che lo SPID e la firma digitale funzionino su telefono deGooglizzato o con Google Play Services containerizzati (su GrapheneOS). Il sistema di firma digitale deve funzionare via browser o, ancora meglio, avere un’app per Linux. Mi ricordo che @jsparber aveva cominciato a lavorare su un’app per Lepida SPID in GTK, ma credo il progetto sia rimasto dormiente.
Sono felice di pagare, ma solamente se si tratta veramente di un’organizzazione ben posizionata politicamente.
Magari @lealternative ha qualche idea? 👀
#PEC #SPID #Italia #ItaliaDigitale #Android #deGoogle #aiuto #mastoAiuto

@tommi mi dispiace ma non sono più informato.
Comunque per Spid chiederei a @quinta (ovviamente) e a @verzulli
In passato Lepida e SIELTE erano tra quelle con le quali si poteva fare a meno di Google.
Per la PEC dovrebbero saperne qualcosa anche @iusondemand e @mariosabatino


#NowPlaying Completely Between The Covers by Matthew Sweet And Susanna Hoffs on Edsel Records from 2015. This is a really nice 4 CD set with 60 cover versions from the 60’s, 70’s and 80’s. Picked this up at an auction a few weeks back, nobody else bid on it so got it for £10. Currently part way through the 60’s disc. I think I only became aware of Sweet/Hoffs because @TheVinylApe posted something about them a number of months back. #CD


@Keironmb dude….
TEN BUCKS?!?!
What a steal!!!!


I have such a hard time recalibrating expectations when my schedule changes like this. On a normal day, I would be a little more than halfway through my shift. Today, I've barely put in an hour.

@neatnik omg 😂

I have this very clear memory of another organizer scoffing that the notion that there should be snacks... at a meeting of the leadership where they had a catered lunch.
Look at any big fancy conference. There isn't just food served, it's nice food. Because when it's important people serving a nice luncheon saves time and they are important busy people.
When it's a community meeting it's suddenly "free stuff" and the first expense to be cut.
@futurebird
Interesting observation, and re: snacks excellent points.
Alice McFlurry :bc:
boosted


My favorite snack-time tradition is when my husband opens a bag of potato chips and gives me the first one as if I’m receiving my holy communion.


https://steamcommunity.com/discussions/forum/10/571553842245699531/
here's someone comparing Steam's rule against sexualizing children to the Holocaust I guess
Coffee (Team CW)
boosted


"Mashable: Samsung TVs might use the mics of connected devices to listen to you, researcher says. “On the social media platform X, cybersecurity researcher @log4j shared that an investigation into Samsung smart TVs found that televisions without a mic will scan for connected devices that are equipped with a microphone. The smart TV will then utilize the audio data collected from the soundbar or other connected Bluetooth devices.”"
https://researchbuzz.me/2026/11/02/korea-times-canada-readerfunded-camerakit-lenskit-more-monday-researchbuzz-november-2-2026/
