jwz
boosted

Oof, I laughed a little too hard
Discussion
Oof, I laughed a little too hard
The registrar from the domain has email addresses support@spaceship.com and abuse@spaceship.com. Email them to let them know ao3.life is committing theft at a massive scale so they can take the site down.
AG Nessel Challenges MPSC Approval of DTE’s Google Data Center Contracts https://www.michigan.gov/ag/news/press-releases/2026/10/30/ag-nessel-challenges-mpsc-approval-of-dtes-google-data-center-contracts
ALERT! If you have ever posted anything to AO3, it looks like some shitstain has scraped the entire thing, loaded it into an LLM and generated PDFs and audiobooks, which people can buy.
This vibe-coded piece of shittery is ao3.life and if you want to request your works taken down it says you can email legal@ao3.life and they will take it down, but I'm afraid it already looks like they have fed it to an LLM.
This includes ALL my locked fics, btw.
@BestGirlGrace @sierrashark queen peach
⬇️ not a princess
This was a project we run ten years ago, we did not get the funding but set it up anyway. Offering a real alternative to the dotcons world https://hamishcampbell.com/offering-a-real-alternative-to-the-dotcon-world/
$TOOT  +1.88 78.45 #TrendingNow #Crypto #BTSE
Update on the 9.8 CVSS TCP/IP RCE in the Linux kernel (CVE-2026-98432): we've detected what appears to be a threat actor activity scanning the entire internet for exposed affected systems. Our own scanning also suggests that the number of potential targets is high, therefore there is an increased likelihood of threat actors attempting to develop exploits for the vulnerability.
while CVE-2026-98432 is believed to require MPTCP to be enabled in the kernel, as well as a listening app/service which binds an MPTCP socket, which many have suggested should be rare, several kernels including Debian enable MPTCP by default.
Additionally, Go 1.24+ binds MPTCP sockets by default if the option is enabled in the kernel, so anything built on top of Go (including Caddy) will create the required MPTCP listener.
The mitigation of setting net.mptcp.enabled=0 disabled MPTCP, but does not apply to existing sockets, so any applications that have bound MPTCP sockets need to be restarted, otherwise the system remains exploitable.
You can check if your server is running any MPTCP listeners with the following command: sudo ss -Mlnp
On 2026-10-30 our preliminary internet-wide scan of port 443 confirmed that there are approximately 2,102,043 servers that are successfully reachable via an MPTCP connection. A deeper scan which attempts to connect to each endpoint on port 443 and negotiate a full TLS connection with MPTCP enabled returned about 762,774 systems.
Neither scan can confirm that these are unpatched kernels, just total exposure, but it's a lot more systems than expected. Since a valid HTTP connection is not required to exploit the vulnerability, the total attack surface is likely closer to the 2.1 million number than the 763k one.
As of today (2026-11-02), we've picked up several residential proxies and VPNs scanning the internet on port 443 using MPTCP-enabled connections. Since regular scanners do not negotiate MPTCP by default, and no data is being sent to the HTTP server over 443, we strongly suspect this activity is scanning for CVE-2026-98432 specifically. The use of residential proxies and RU-based VPN servers suggests that this is likely threat actor scanning, rather than security researchers.
Currently there are no known publicly available remote code execution exploits, but there are several denial of service proof-of-concepts floating around. This code gives threat actors a starting point to begin attempting to weaponize the vulnerability. Building exploits for the vulnerability is reported to be extremely difficult, but several state-sponsored threat actors likely have the resources required to succeed.
i was more worried when i didn't have access to the software construction machine.
it's like being extra prejudiced when you've never met a foreigner - no prejudice survives contact.
now i have access to a personal software construction machine and i'm not worried anymore.
i feel liberated, and, paradoxically, i feel *valued* as a programmer. *because* of what i learned in the past 20 years, i can use the machine more effectively
a second life has begun. i have time now to live more of it.
@lritter The classic paradigm holds true:
@salva_pl Egun on .☕️ 👋
So for the New York Times information warfare tactics we've got:
1) Front page carpet bombing
2) Scant coverage
3) Bothsidesing
4) Selective tone policing
Anything else?
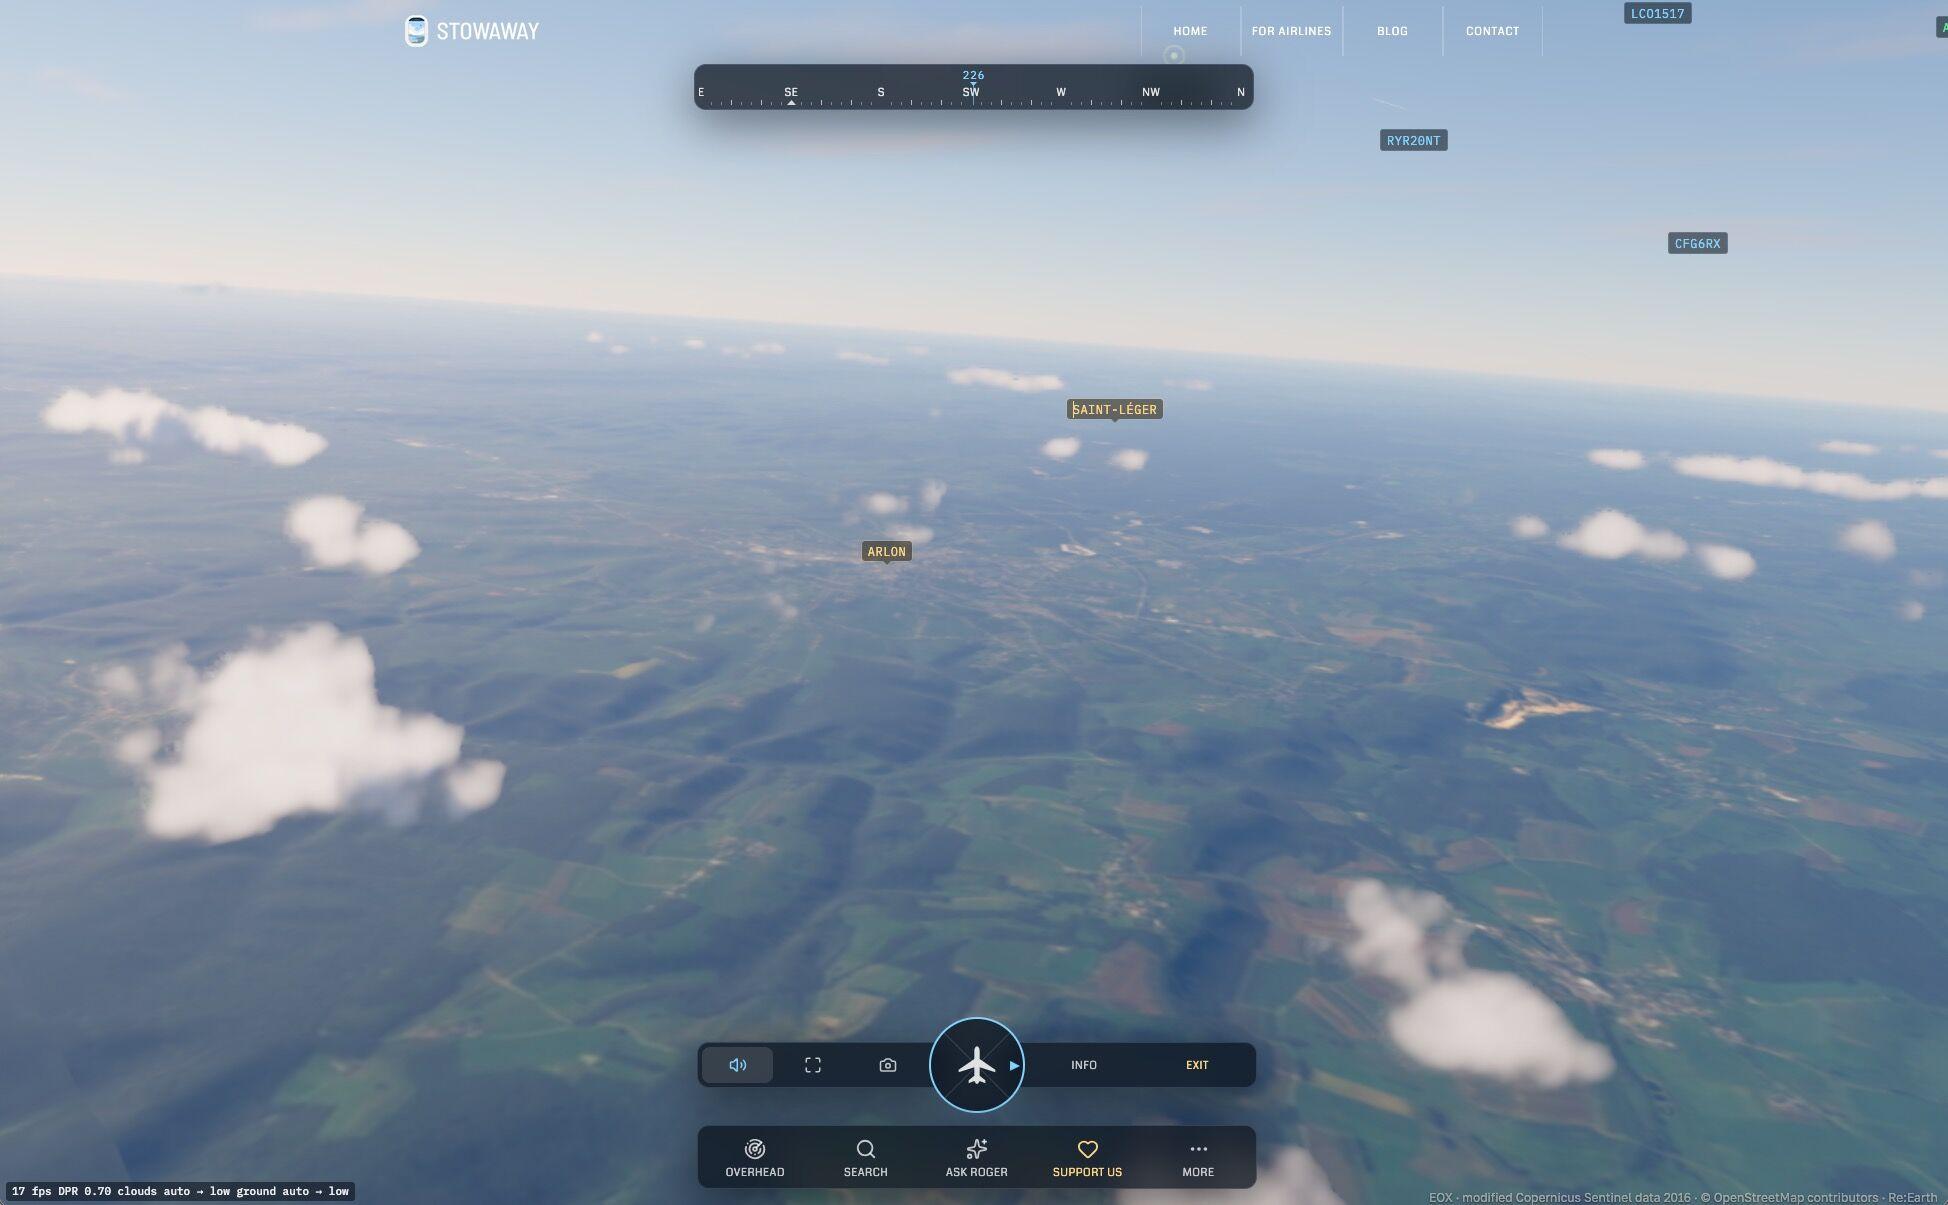
This one is for my flight enthusiast friends: Stowaway lets you tag along real flights in the sky around you, and enjoy a rending, of what the view from this plane would be (based on real data)
@zeborah it's been a while since I visited the global ILS tracker that counted implementations of different software around the world's libraries, but I'd be interested to know whether Koha or Bibliocommons (or whatever the real name of the system Kotui uses) is based on is prevalent. Given that more than a few entire countries around the world (Turkey?!) have deployed Koha nationwide, it does seem a real shame that the land of its birth & cultural home has given it the cold shoulder.
@zeborah I wonder if this rather topical thread might shed any light: https://mastodon.nzoss.nz/@lightweight/117551373432104733
An alternative option would be to have a --search-path option, and any relative paths would be searched there. That would mean that the configuration itself does not need to be aware of search paths at all.
So... if the default search path is:
././share./share/etc{dirname(argv[0])}/../share{dirname(argv[0])}/../share/etc/run/iocaine/etc/iocaineThat should cover both the configuration file (defaulting to iocaine.kdl), and the default script & module paths (nam-shub-of-enki/pkg.roto and nam-shub-of-enki/module, respectively).
In the repo, I'd have a share directory that contains etc/iocaine.kdl, and nam-shub-of-enki, so the third path would find the config file, the second would find NSoE, when run with cargo run.
On distributions that follow FHS, one of 4-7 would likely land at the right place.
When using a relocatable tarball, 2 & 3 would find the right files too.
The advantage of this whole thing is that I don't need to implement Blueprint::default(). I'd still need a default impl for script, so that one could write:
http-server default {
bind-to "127.0.0.1:42069"
}
And it would use the default script. But that's less bothersome to do that Blueprint::default().
@zeborah (and by 'you' in 'you make it better', you can be 'anyone' in the world, which is how Koha works, fittingly)
@zeborah it's been a while since I visited the global ILS tracker that counted implementations of different software around the world's libraries, but I'd be interested to know whether Koha or Bibliocommons (or whatever the real name of the system Kotui uses) is based on is prevalent. Given that more than a few entire countries around the world (Turkey?!) have deployed Koha nationwide, it does seem a real shame that the land of its birth & cultural home has given it the cold shoulder.
@andre Hätte man das Prüfverfahren angefangen als die Einordnung als in Teilen rechtsextreme Partei erfolgte, wäre es heute wohl schon fast durch.
@jwildeboer Glaub ich nicht. Beim NPD-Verfahren lagen zwischen Antrag 2013 und Urteil 2017 fast vier Jahre, und der erste Anlauf ist 2003 sogar komplett an den V-Leuten geplatzt. Bei einer Partei mit 20 Prozent und Abgeordneten überall wär das eher länger gegangen, und die AfD hätte die ganze Zeit ihr Opferding durchgezogen.
@sigmasternchen @ryanc yup, most of the time it's potassium chloride. Not sure how that would be achieved for sea salt though.
 Posted in
Fediverse
Is there a way to not see duplicate of the same topic across different communities?
Hi everyone!
I’m really enjoying the Fediverse through Lemmy and Peertube.
One creator I enjoy and follow on the Fediverse is Gardiner Bryant as his content is really enjoyable.
Sadly he ´s the target of my post as he shares his content on many different communities that I follow.
Today I had 5 times the same topic on RetroDeck (great project too) on my feed on Lemmy (Voyager).
It is the same on PieFed (Interstellar).
This is really annoying and I haven’t found a way to not show these duplicates. Do you know about one or is it worked on?
Also when crossposting, it would be great if everything appeared under on post. Is it feasible?
Sorry if it’s easy and I just missed it. In a way I hope it is because it would mean that the Fediverse is festure rich😇
Posted in
Fediverse
Has anyone here used or maintained Flohmarkt?
What was you experience like? Did you use the built-in messaging? Did you feel that it respected your data privacy enough?
If you maintained one, did you have any major issues or concerns?
I’d love to have an alternative to fb marketplace but nothing seems to be as user-friendly to get people using it. I would love to eventually start a server if it is doable for a semi-capable person.
Sorry, the app encountered an unexpected error