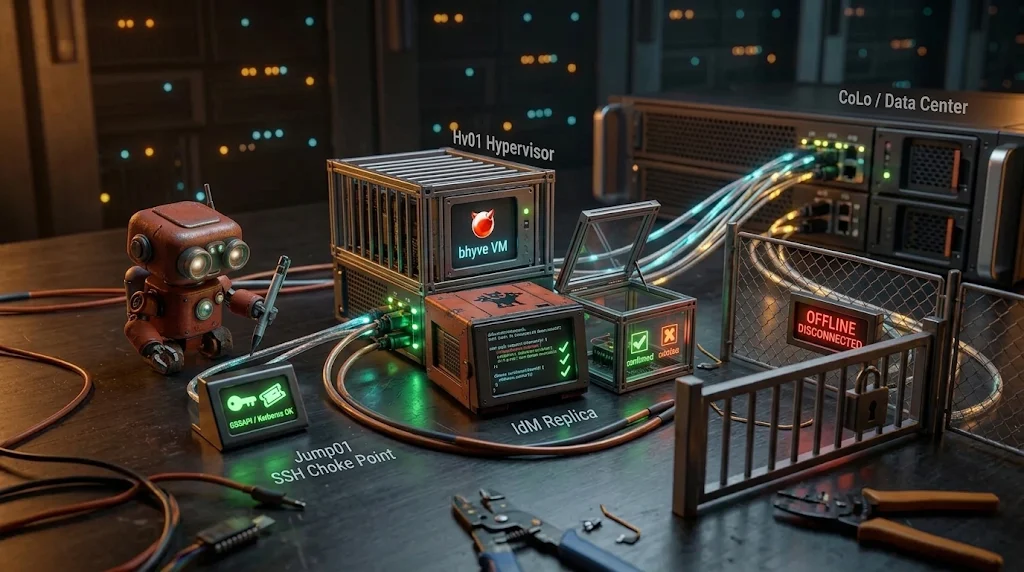

My two IdM servers live in a data center. Every SSH login at home depended on a WireGuard tunnel to reach them. Tunnel down, tickets expired, locked out of my own hypervisor from my own sofa.
So: a third IdM replica in a bhyve VM at home. A DMZ that only exists inside the host, a tunnel that only worked one way, and DNS locations that were less location-aware than I thought.
https://blog.hofstede.it/an-idm-replica-at-home-kerberos-that-survives-a-dead-tunnel/