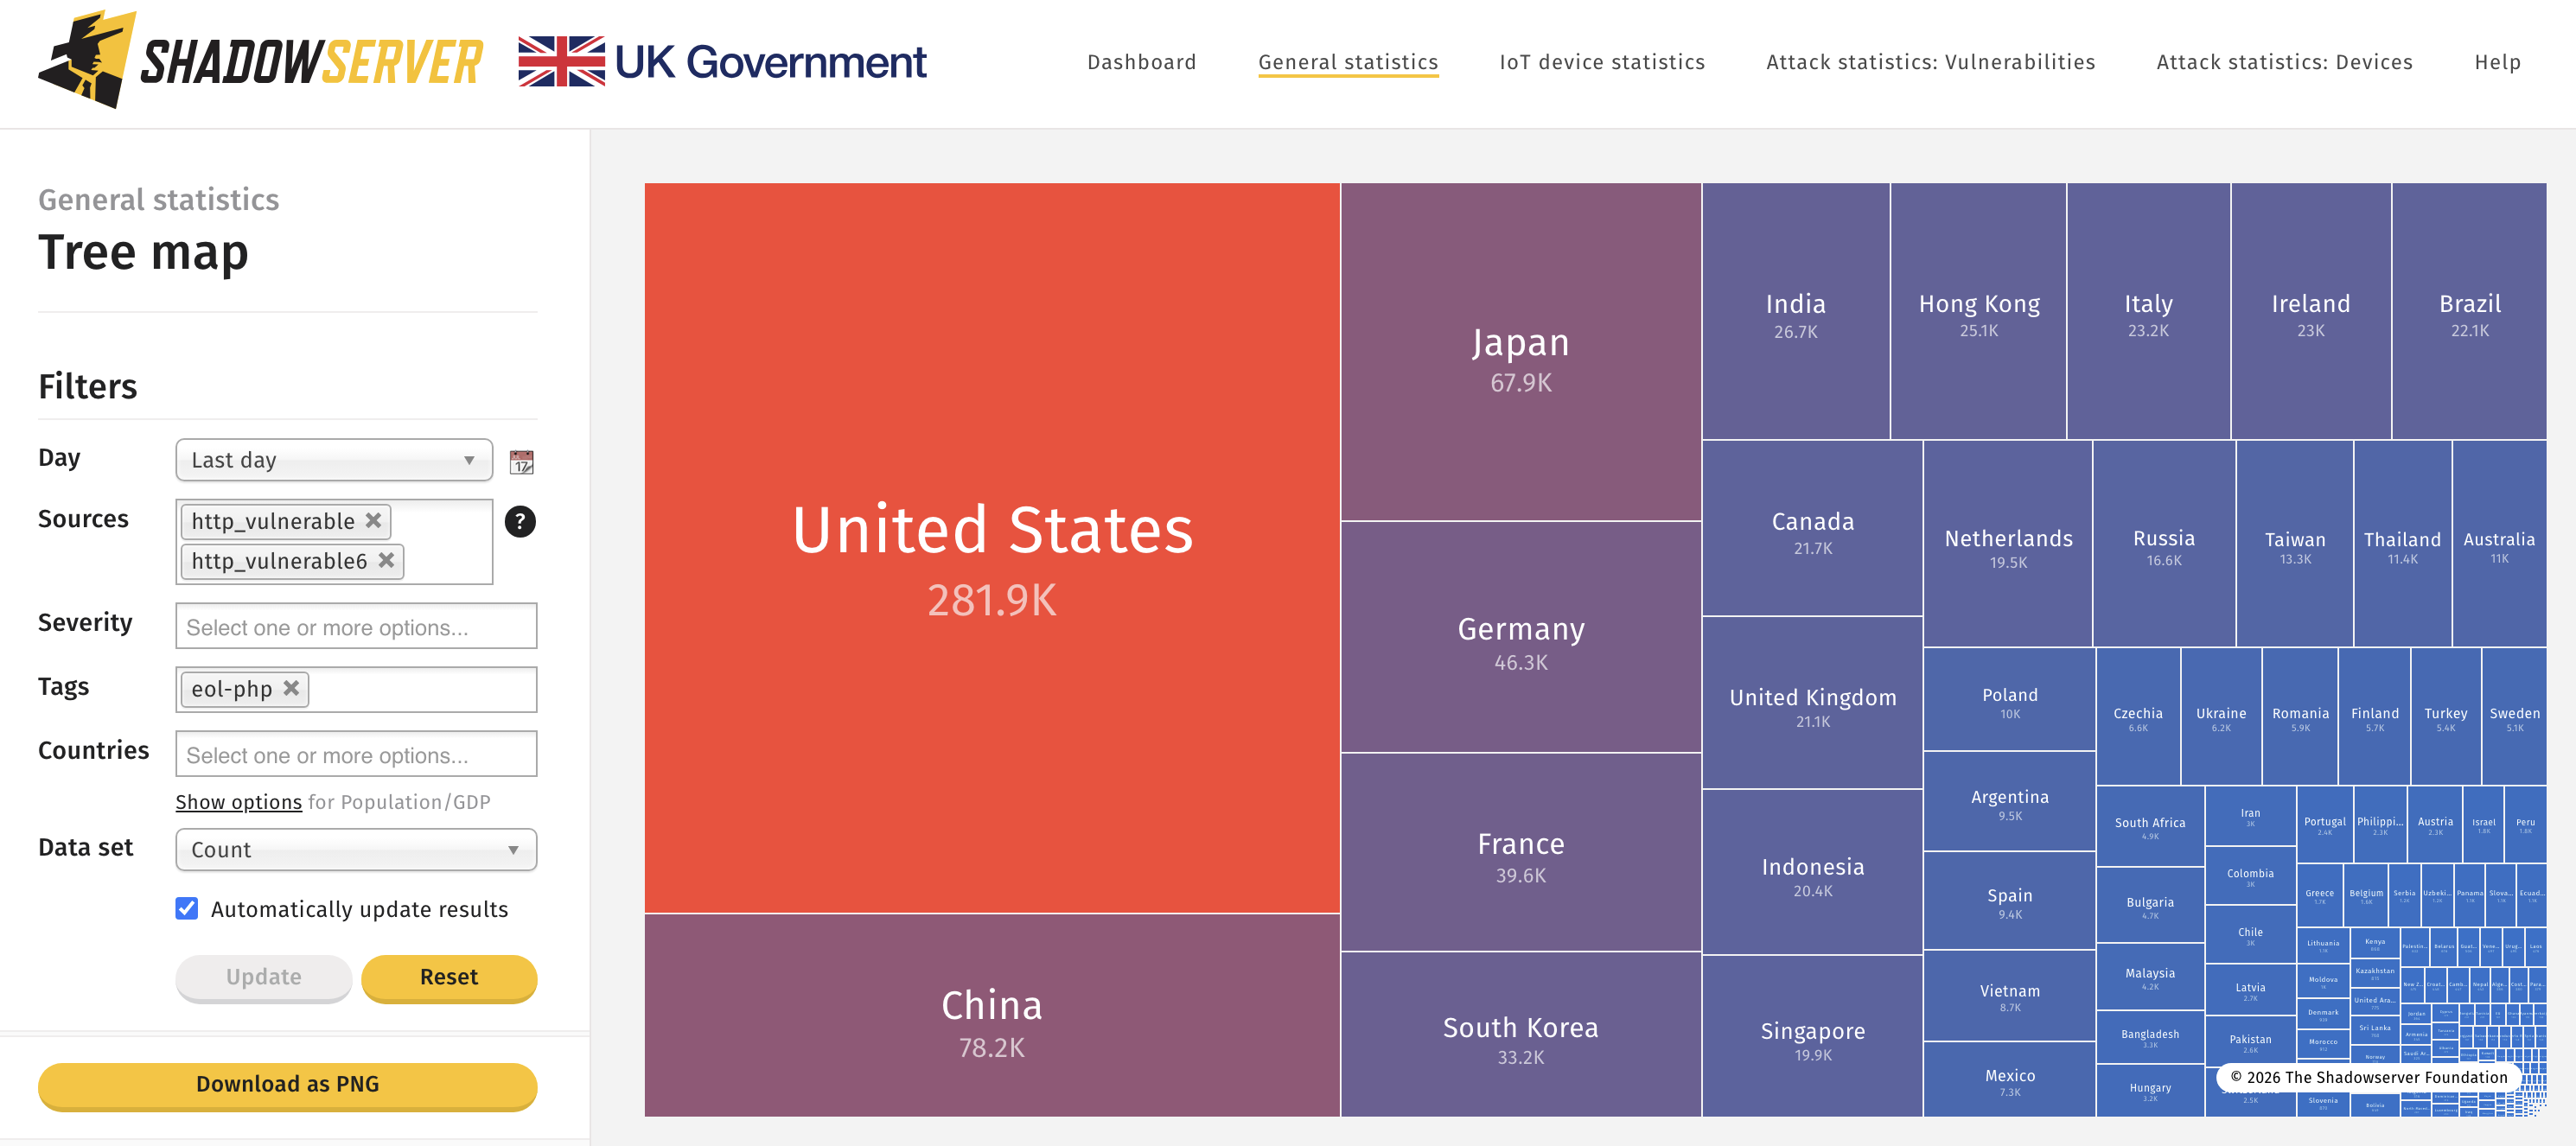
PHP Attacks Update: As others, we have been observing a lot of AI slop PHP attempts against our honeypot sensors the last week, but so far no confirmed exploitation.
We have also refrained from CVE-2026-109618/619 tagging in scans, due to lack of reliable, safe large scale methods.
Instead we have opted for reporting out End of Life instances, which is hopefully the more actionable approach at this stage. We added 'eol-php' to the Vulnerable HTTP reporting. Tagging is based on: https://endoflife.date/php (anything older than 8.2)
You can track unique IPs running EOL PHP (not hostnames) at https://dashboard.shadowserver.org/statistics/combined/tree/?date_range=1&source=http_vulnerable&source=http_vulnerable6&tag=eol-php%2B&data_set=count&scale=log&auto_update=on
Make sure to update those systems!