Relay for mastodon.online
boosted

Boost:
Unknown type of activity/object
Discussion
Unknown type of activity/object
‘Java is the beating heart of the modern economy’
❤️💓☕️❤️💓☕️❤️💓☕️❤️💓☕️❤️💓☕️
sounds like it's in Base64 ?
(gift) https://www.nytimes.com/2026/11/17/us/politics/ai-security-bug-java.html
Same USMNT lineup as Saturday: Kochen; Freeman, Trusty, Richards, Robinson, Adams, Berhalter, McKennie, Tillman, Hall, Pulisic.
Five subs allowed.
With Orlando playing an MLS playoff Thursday, Justin Ellis is not in uniform.
Unknown type of activity/object
Sooooo excited for @fenn.ink@bsky.brid.gy birthday… 🎉 Gunna eat some good cake 🙂 No I won’t elaborate
Unknown type of activity/object
Me watching the Internet fall apart this week
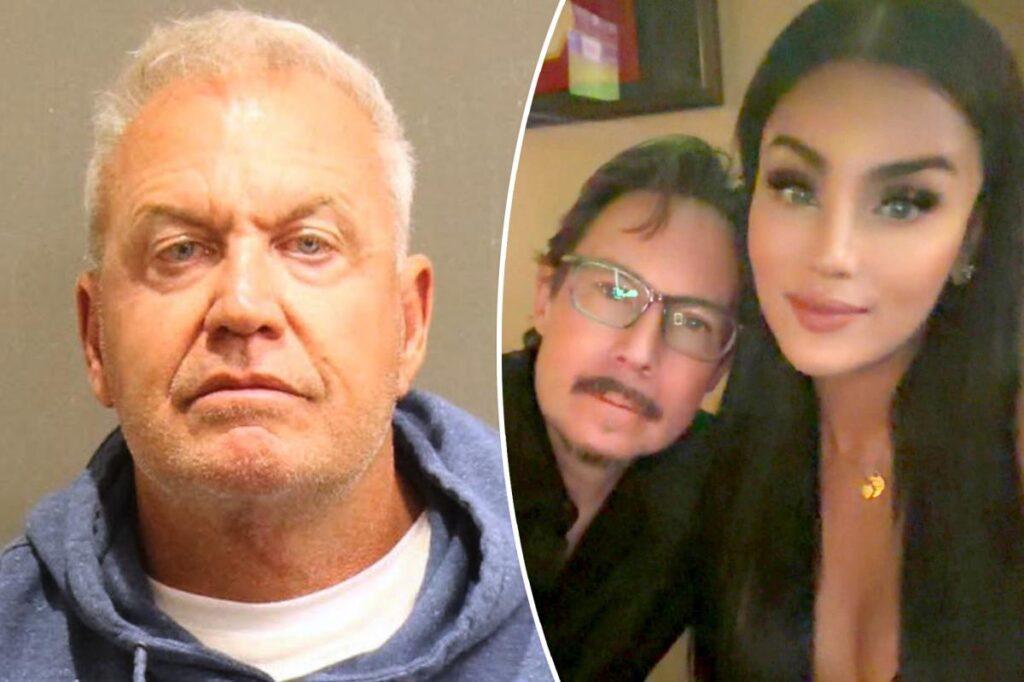
Lawyer, wife’s furious 911 call revealed after Rex Ryan allegedly ran over their feet: ‘Small penis’ https://www.rawchili.com/nfl/1057488/ #California #Football #NewYorkJets #NFL #RexRyan #Sports
You think this cold is going to stop me from my evening Vermut? Ha!
@bigzaphod Lots of early electronic games had no computing! Pong is just circuits. There's pinballs & Moon Landers. Even with chips, Merlin's like a calculator chip, does a bunch of games.
@mdhughes @bigzaphod I remember the first time I saw Pong in the wild.
Al Carns MP lays out the challenges across the globe, and the conflicts that continue to rage.
We face a volatile and dangerous world, we must build partnerships on defence and economic security with out closest allies across the Channel.
MORE😤
@libreleah how would you make secure boot work better with free distros?
@esoteric_programmer well, nothing in what i wrote suggests improvement to the secureboot specification or its implementation - in fact, it would remain precisely the same. i was talking about use of it in conjunction with encrypted esp. unlock esp at boot. this can work by having a fake boot option in the edk2 menu that does the same as "cryptomount -a" in grub, unlocking all volumes (alternatively run it in edk2 shell with specific partition as argument). it would always return error on unlock, so that it loops through boot options - and the normal loop that does boot volumes would refresh after unlock, so you could have unlocked boot option in boot order for example.
this can be done by porting the luks/libgcrypt code from grub. this alongside things like the raid drivers in grub.
use of encryption here means that nobody can see what's on your esp. this can thwart certain evil maid attacks. you prevent modification of boot files. then normal secureboot - nothing changed there.
In theory yes, but now all I see is dog shit lurking underneath 🫣
Sorry, the app encountered an unexpected error