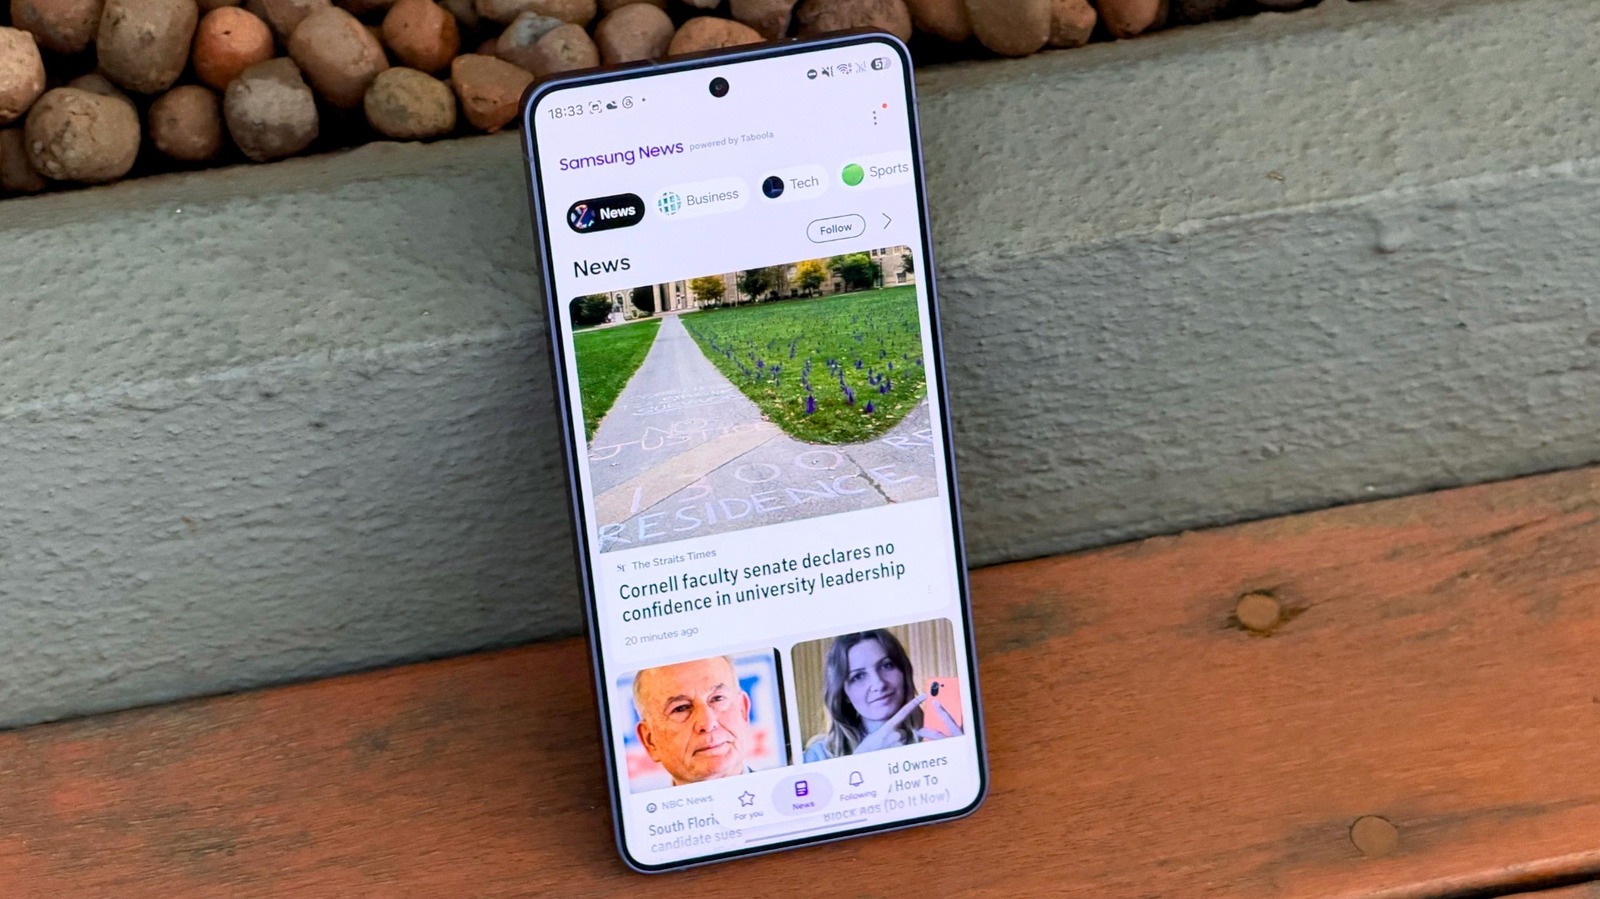
The Samsung News app is on its way out — in South Korea and India for sure, and possibly in other markets too. Here’s @Engadget with more, and what to do if you’re a Samsung News user (have you heard of @Flipboard?).
@firefly @czarbucks @amyedge @AE4WX @ai6yr 16 lbs squared pressure…
I wish Mastodon had a mute-ish option. Where it randomly shows someone I follow on my timeline. I like following them but 10 posts days is too much. Maybe there is already something like this. I like that Mastodon doesn't have a "algorithm", but I wish I could create my own algorithm based on rules.
@grumpygamer Every time I see a post like this, it's so hard for me to not read it as "That Cheese guy sure posts a lot of bird photos"
I think this'd be a nice feature. I found this suggestion ticket on GitHub (mostly focused on hashtags, but also accounts), but it doesn't have much activity https://github.com/mastodon/mastodon/issues/35799
NY Times: United Halts Flights as It Addresses ‘Widespread System Outage’
(Nov 16, 2026 2:22pm PT)
Jonathan, a 194-year-old Aldabra giant tortoise, was born before the Civil War. Scientists have now sequenced his genome to reveal what’s behind his extreme longevity, so we can live longer too.
This, basically.
The HTML Details That Make Forms More Accessible - Ronalds Vilciņš:
https://ronaldsvilcins.com/2026/10/12/the-html-details-that-make-forms-more-accessible/
Who is an accessibility file for? - Marcelo Paiva:
https://mpaiva.com/writing/who-is-an-accessibility-file-for
Captioned Doesn’t Always Mean Accessible - Christopher Phillips @ WebAIM:
https://webaim.org/blog/captioned-doesnt-always-mean-accessible/
Standards In Progress: Making Video Posters Accessible, Responsive, and an Element - Scott Jehl:
https://scottjehl.com/posts/responsive-accessible-poster/
Band-aid accessibility - Eric Eggert:
https://yatil.net/blog/band-aid-accessibility
CW: "AI" discourse
I like this stance!
@ai6yr and if it does....
People were clamouring about how awesome the ponytail plugin is.
To be perfectly blunt: I think the people who think it's awesome are probably not good programmers.
It codes like an extremely smart, highly ambitious junior software engineer. It's nice for demoes, and provides a rather false sense of reassurance that you can actually spend time reading the code.
But then metaphorically zoom out, and start adding features, then it's where all the shotgun surgery starts to crop up for each feature that we try to introduce and bug that we try to fix.
It eats up context window, burns through tokens, and the overall code becomes worse, partly because of the lost-in-the-middle hallucinations that LLMs are susceptible to.
@manlycoffee 🤔 everything looks like crap is you zoom out far enough...
Sounds semi-useful, maybe not "awesome".
At least I now know it isn't a fake man-bun 😆
#np: nation of language - inept apollo
Wiz's data says 64% of cloud environments have resources vulnerable to it, a figure that does not take configuration into account.
Two teams found it. The Hacker News reports Anthropic's OSS Scanner reported the flaw on October 26, and Wiz says Google Cloud's Vulnerability Research Team independently discovered it as well.
If you manage a server, run httpd -v and compare it to the range.
If you can't update yet, Cybersecurity News says one option is to limit the server to HTTP/1.1 until the update is done, and The Hacker News quotes Wiz's version: remove h2 and h2c from the Protocols directive. If a host runs your site, send them the CVE number and ask for the date.
Check the version today, and ask your host in writing.
The Hacker News reports that Red Hat says public research has demonstrated a reliable exploit, though it does not name or link that research. Treat the Wiz line about no exploit as a snapshot from publication day.
The affected versions run from 2.4.55 through 2.4.70, and Cybersecurity News says the fix came on November 11 in 2.4.71. Cybersecurity News adds that Apache describes it as a concurrency problem, where shared resources are used without proper locking.
Wiz's data says 64% of cloud environments have resources vulnerable to it, a figure that does not take configuration into account.
Two teams found it. The Hacker News reports Anthropic's OSS Scanner reported the flaw on October 26, and Wiz says Google Cloud's Vulnerability Research Team independently discovered it as well.
If you manage a server, run httpd -v and compare it to the range.
Apache's HTTP/2 Bug Lets Strangers Run Code on Your Server. Check Your Version Today...
Wiz published a warning on November 11 about CVE-2026-119618, a critical flaw in the HTTP/2 module of Apache HTTP Server. Wiz says a remote, unauthenticated attacker can corrupt heap memory and run arbitrary code, and that when it published, no exploit was available and no attacks in the wild had been reported.
The picture has moved since.
The Hacker News reports that Red Hat says public research has demonstrated a reliable exploit, though it does not name or link that research. Treat the Wiz line about no exploit as a snapshot from publication day.
The affected versions run from 2.4.55 through 2.4.70, and Cybersecurity News says the fix came on November 11 in 2.4.71. Cybersecurity News adds that Apache describes it as a concurrency problem, where shared resources are used without proper locking.
Apache's HTTP/2 Bug Lets Strangers Run Code on Your Server. Check Your Version Today...
Wiz published a warning on November 11 about CVE-2026-119618, a critical flaw in the HTTP/2 module of Apache HTTP Server. Wiz says a remote, unauthenticated attacker can corrupt heap memory and run arbitrary code, and that when it published, no exploit was available and no attacks in the wild had been reported.
The picture has moved since.
If I were to venture a guess of what happened, I would presume MySpace and Facebook’s rising popularity stalled LiveJournal’s growth in the Western English speaking market and split people’s attention. At the same time, the Russian side of the website was growing in popularity. When it was sold, I remember a lot anger around personal data being sold to a Russian entity and a lot of debate about free speech. After that happened, LJ became practically a ghost town overnight amongst the English speaking population. To me though, I feel like Tumblr was the closest successor in spirit to LJ.
Good point about Tumblr! It definitely was. I don’t remember hearing anything about LJ then, but I bet it was quite a debate. How times have changed! Now we have Inkwell. 😊
nanoserde
Pros
- 483k recent downloads
- no serde
- no dependencies outside of
nanoserde-derive. - Don't see AI taint in the repo
- Can also serialize / deserialize from JSON, without serde, which might be useful for
iocaine
Cons
- Maintainer is on Twitter (but also on Mastodon)
- Maintainer appears to have started playing with agentic coding a few months ago. Not on nanoserde, but elsewhere. No idea if they stopped, or what their current stance is. Worrying, nevertheless.
Opinion
God fucking damnit. Would have been so nice, but I'm not looking for something that can become slop any moment.
wincode
Cons
- Depends on thiserror (but I already have that in my dep tree, so no big deal).
- Developed by blockhain folk
Opinion
Not even gonna look at the pros. Blockhain folk, on Twitter and GitHub? Fuck off.
I don't think people are aware of how bad the AI bots have become on Mastodon in the last weeks. I would estimate that, out of 200 signup attempts, 199 are bots now. They are still mostly recognizable, thus blockable, but it's not getting better. #mastoadmin
The Samsung News app is on its way out — in South Korea and Indie for sure, and possibly in other markets too. Here’s @Engadget with more, and what to do if you’re a Samsung News user (have you heard of @Flipboard?).