Posted in
Fediverse
Closed source and clearly completely vibe coded? Just look at the site, it reeks of AI. Even this post has so much AI-speech.
Yea, no thanks.
Discussion
Posted in
Fediverse
Closed source and clearly completely vibe coded? Just look at the site, it reeks of AI. Even this post has so much AI-speech.
Yea, no thanks.
OpenRCT2 lets friends build the same RollerCoaster Tycoon 2 park
https://lockergnome.com/openrct2-rollercoaster-tycoon-2-cooperative-parks/
In this episode Data loses a valued crewmember we've never heard of before on an away mission although actually is the true source of anime on Earth.
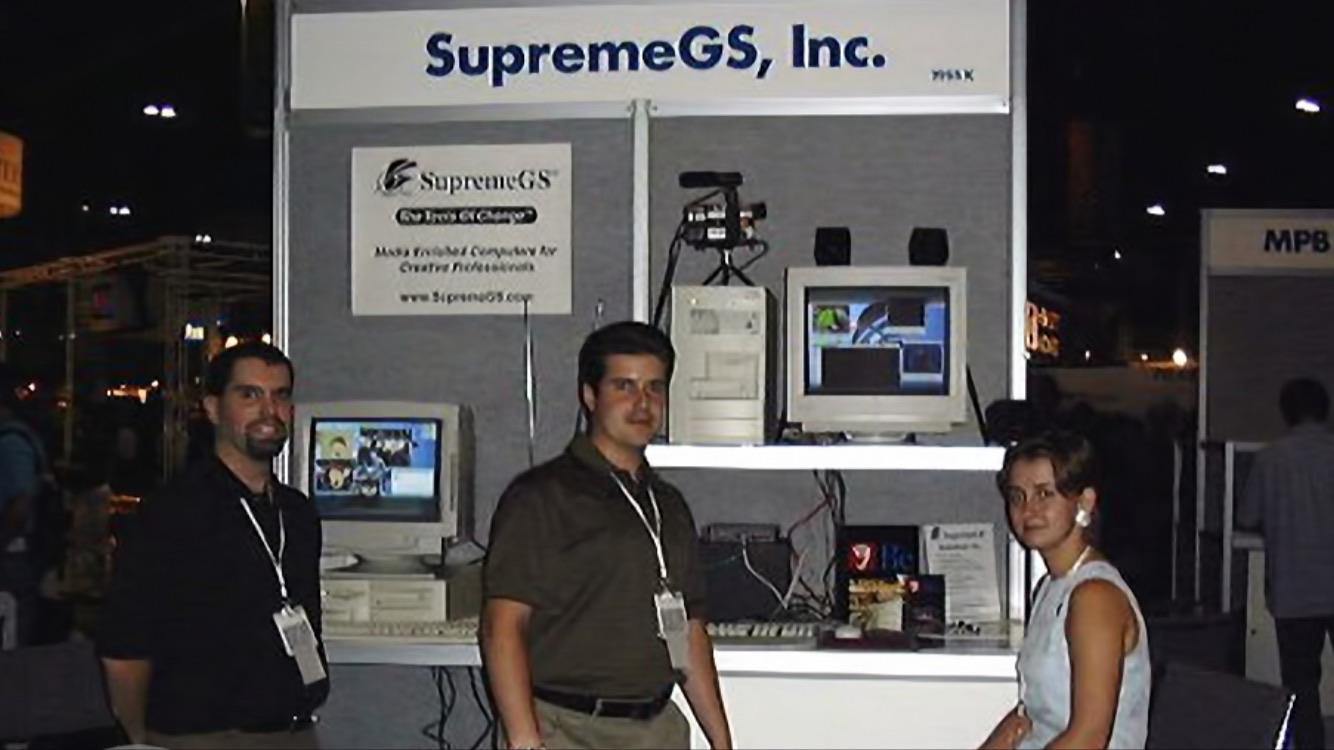
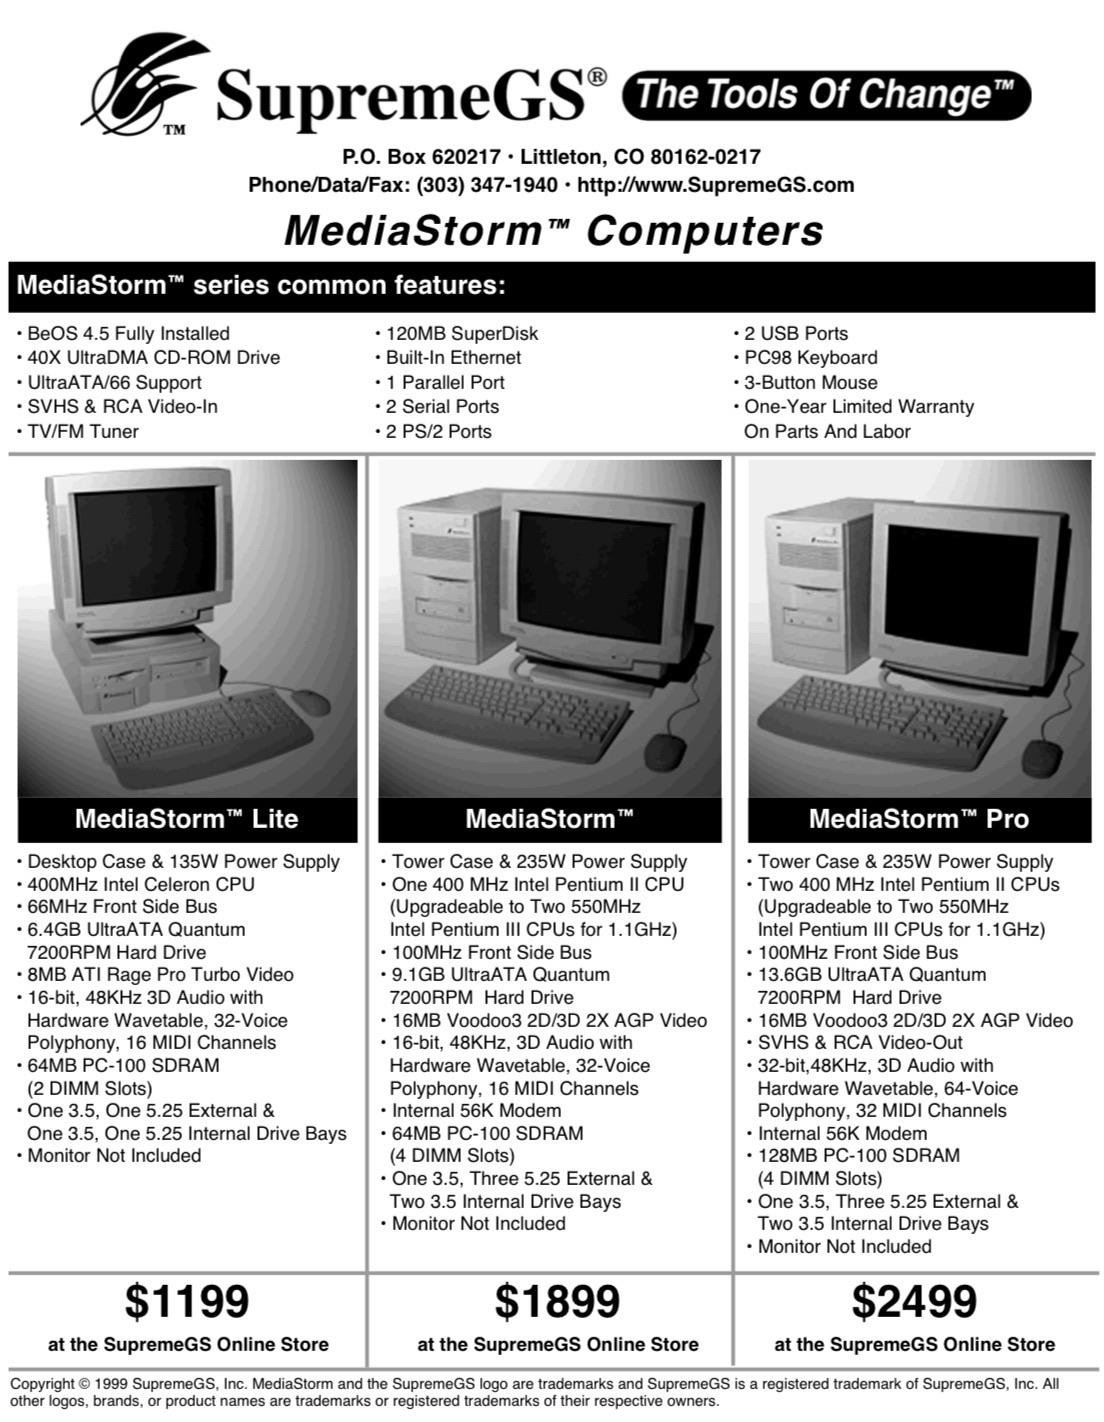
Back in 1999-2000, my friend (middle, first pic) tried to launch a company focusing on BeOS-based computer systems targeted at media creators. Our small team went out to SIGGRAPH '99 in L.A. to hopefully kickstart it. Obviously, that didn't happen, but I did briefly meet Jean-Louis Gassée.
Anyway, it was fun to see a BeOS reference for the first time in ages. Thanks for that!
Posted in
Fediverse
not really, no.
Posted in
Fediverse
It's a shame you see it this way, Andy Piper disagrees but you're free to think as you wish, it's an open forum :)
tailwind doesn’t have the centered highlights, on container borders, but every vibecoded site does.
鍋ぱーちーが必要
OpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
https://openssh.com/releasenotes.html#10.6p2
If you operate a Linux system that uses musl libc without PAM (Alpine Linux is one example) then stop reading and set PasswordAuthentication=no or disable SSH for these systems IMMEDIATELY.
This vulnerability does not exist on non-Linux systems, Linux/glibc systems and Linux systems that use PAM for password authentication.
We consider the root cause of this bug to be outside OpenSSH itself, but we're in a good position to deliver a mitigation quickly.
We are making this release as fast as possible (we learned of the problem yesterday) because we have recently observed multiple cases of rapid bug rediscovery by AI agents, sometimes within hours, and so now consider long embargo periods to be a dangerous practice that primarily benefits attackers.
Thanks for Özgün Kültekin of Wakefield (wakefield.co) for reporting this problem to us and for the Alpine Linux developers for making an updated release available at very short notice.

Posted in
Fediverse
It’s wild that just the thumbnail alone can tell you it’s vibe-coded.
Posted in
Fediverse
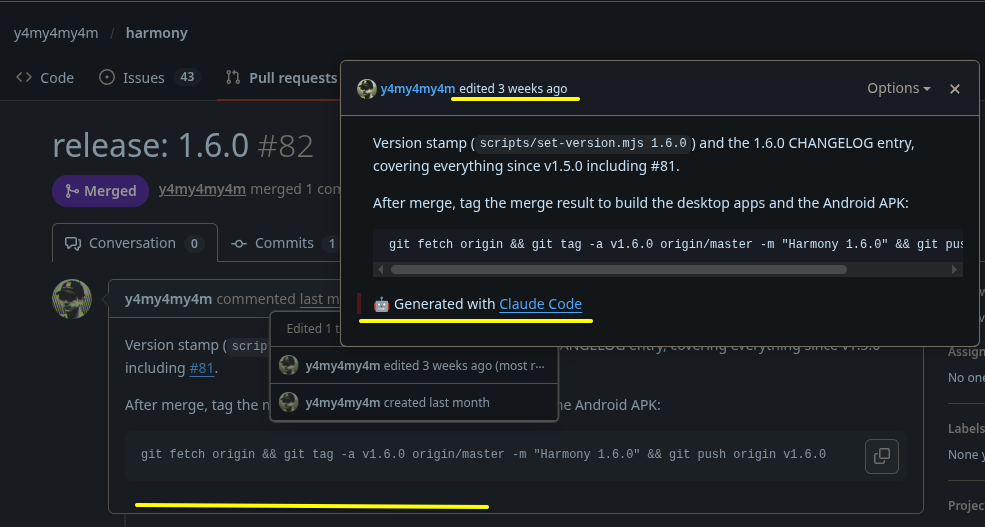
It was. And they’ve also erased its generated disclosures.
![] (https://media.piefed.social/posts/hR/wy/hRwyr37MeWjePRc.png)
Posted in
Fediverse
If the author’s profile is any indication, it’s likely Harmony was written using AI:

Elon Musk admits Grok Bot costs too much to serve
saying the costs part out loud
by Amy Castor and David Gerard
https://www.youtube.com/watch?v=wJb0JsK3ufM&list=UU9rJrMVgcXTfa8xuMnbhAEA - video
https://pivottoai.libsyn.com/20261104-elon-musk-admits-grok-bot-costs-too-much-to-serve - podcast
time: 6 min 25 sec
https://pivot-to-ai.com/2026/11/04/elon-musk-admits-grok-bot-costs-too-much-to-serve/ - blog post
@davidgerard old an unnecessarily flattering pic of him!
Posted in
Fediverse
Hi, I got a couple questions that aren’t answered on your transparency page yet.
It just occurred to me: We don't really have corrupted downloads anymore, do we? Like, random bit flips and stuff?
Back in the day (I'm talking 2000s) they were much more common.
And now I wonder whether the hardware has gotten better (and less analog), or whether it's because we're using HTTPS for everything now, or a combination of both, or something else entirely.
@scy ECC (error correction coding) on lines is now way more common and fiber connections are close to error free.
Posted in
Fediverse
Has AI been used to create this?
Do you really need to ask? 😅
DuckDuckGo pitches itself to schools amid backlash over Google’s AI policy https://techcrunch.com/2026/11/04/duckduckgo-pitches-itself-to-schools-amid-backlash-over-googles-ai-policy/
I don't want to say "I told you so", but...
https://mastodon.sdf.org/@ParadeGrotesque/117553406325652075
Posted in
Fediverse
Good question, however the security model doesn't depend on the code being secret, and it shouldn't. The auth, signatures, permissions and input handling are standard and went through an OWASP review before launch.
What's closed is the anti-abuse layer, spam, rate-limit tuning, the signals for detecting ban evasion and coordinated accounts. Those work partly because spammers don't know the exact numbers. Lemmy's and Mastodon's are public and they get played for exactly that reason. Hope it helps :)
not really, no.
Sorry, the app encountered an unexpected error