Posted in
Fediverse
Sean Tilley
liked this activity

Well they didn’t seem to have much to say?
Discussion
Posted in
Fediverse
Well they didn’t seem to have much to say?
The "Justified police shootings"...
Geheimer Polizeivertrag mit den USA: Entscheidungen, die Menschen erheblich beeinträchtigen, dürfen auch per „KI“ fallen https://www.nd-aktuell.de/artikel/1203304.grenzpartnerschaft-dobrindt-ministerium-schweigt-zu-us-zugriff-auf-polizeidaten.html
On vient de me rappeler qu’aujourd’hui, j’ai l’âge de mon année de naissance.
J’ai pas fait exprès, mais je crois que ma #sieste a duré [mon âge] minutes. C’est sûrement un complot (puisque visiblement tout est un complot).
Kompromittierte Schlüssel gefährden TLS-Verbindungen - Acht private Schlüssel der Zertifizierungsstelle Emuhdra, mit denen sich Webseitenzertifikate signieren lassen, können mit trivialen Methoden geknackt werden. Bisher ist nicht öffentlich wie genau, aber ich hab es sehr schnell rausgefunden. Mein Artikel bei Golem: https://www.golem.de/news/web-zertifikate-kompromittierte-schluessel-gefaehrden-tls-verbindungen-2610-214314.html
Posted in
Fediverse
TIL the fediverse basically DDOS's sites when you share a link.
I shared a link from NPR Tiny Desk but there was no image preview or video embed. After investigating this I learned that when you do that, each instance picks up the link and individually retrieves the link preview nearly simultaneously. For gargantuan sites like YT or Reddit, this is a trivial amount of traffic and not a problem, but for smaller sites like NPR this results in a sort of botnet DDOS attack on the site’s servers. More here. Another example here . For that reason, NPR has blocked Fediverse servers like Mastodon.
I have experienced this on my personal server as well (DDOS), but at the time didn’t know why, exactly.
This isn’t the end of the world, but certainly is not great and hurts engagement with the content. Is there a solution for this? Perhaps using some sort of webtorrent service like PeerTube where they just fetch the information from another fediverse server instead of the source server? Maybe fetching embeds client-side? At least that would stagger the requests.
Every time I see a vibe coder say something along the lines of "if you haven't used these tools over the past five minutes, you don't know what they're capable of, because everything's different now!" I get a little bit perplexed.
You do know that we can see the output without using it ourselves, right? Some of us are still reviewing pull requests and reading through code repositories, y’know?
@baldur I don't have to hug the cactus to know it would hurt.
Posted in
Fediverse
Seems abusable though
Exactly
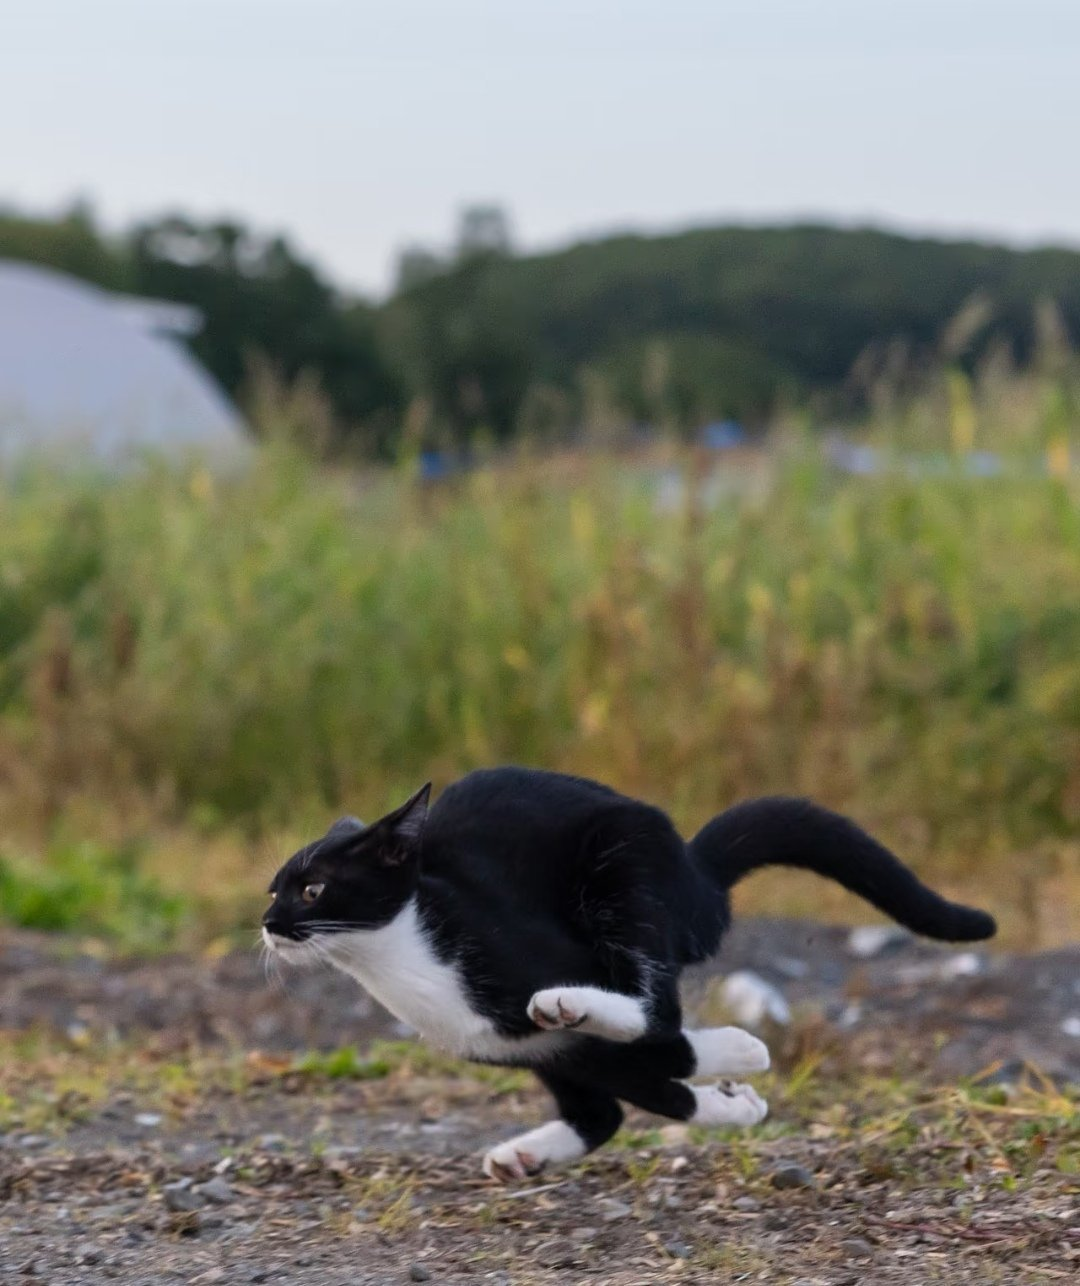
Japanese photographer Masayuki Oki loves cats and travels around Tokyo photographing them.
I've been having mixed results with my AI model on my codebases -- sometimes it finds the obscure bug and fixes it, other times it attempts to rewrite previously correct code into utter garbage, breaking it even more.
🤦♂️
The Gospel according to Peter (Thiel) https://www.theverge.com/tech/1014252/peter-thiel-antichrist-lectures-analysis
Posted in
Fediverse
Yeah, thats how it should be: one download, everyone else downloads from that server, not the original source.
Seems abusable though
@newsmast unfortunately not 😭
Maybe it’s because I’m running iOS dev beta?
Potentially, we'd recommend downloading the production app!
Posted in
Fediverse
That’s not true, you know the data hasn’t been tampered with because of HTTP signatures. The fediverse isn’t just “yolo, just trust me bro”. There are some parts that are a bit more towards that side (particularly with groups on Lemmy) but I don’t think this should be.
HTTP signatures are not a default feature, the baseline is ECDHE key exchange with forward secrecy and deniability.
There isn’t even an official standard for redistributable signed page metadata. There’s just prototypes
Posted in
Fediverse
I have my blog address (which goes to my home server) in my Mastodon profile, and every time I post on Masto, my server gets a request from every Mastodon site that federates with my instance - i.e. hundreds of requests. It’s no problem for my server, because my blog is a static site, but for anything that dynamically generates every single page impression (like worpress or joomla), it could be a problem. Caching settings might help, I suppose.
Truth is, though, I get far more traffic from vulnerability scanners and AI crawlers that don’t honour robots.txt (or aren’t yet listed).
Not Found.

Install Fedizen
Get the full app experience