

帰宅
FediDevs
Circle by
We Distribute
Public
These are the people building the Fediverse!

Anyone can now edit FediDB software (pending moderator review), with a full changelog!
We added a logo to @vernissage and you can see that in the changelog!
https://fedidb.com/software/vernissage
1 more link(s)
@fedidb WOW 🤩. Thank you very much ❤️
Vernissage
boosted
Anyone can now edit FediDB software (pending moderator review), with a full changelog!
We added a logo to @vernissage and you can see that in the changelog!
https://fedidb.com/software/vernissage
pixelfed
boosted
FediDB Apps now can be edited, with optional screenshots ✨


Polls: coming soon to wafrn

@dansup aah yes!
I'm gonna add the instances to my account for easier support ❤️
mirlo.space
boosted

RE: https://mamot.fr/@sknob/117451332769367273
That was an epic listening party !
You can follow the amazing @Traiken right here and get his albums on @mirlo and that other site :)
👉 https://mirlo.space/traiken/
👉 https://traiken.bandcamp.com/
Wow, the latest @pixelfed update just killed my profile (iOS). What happend?? @dansup@pixelfed.social @dansup
@norabjds @pixelfed @dansup@pixelfed.social try now!
Eugen Rochko
boosted
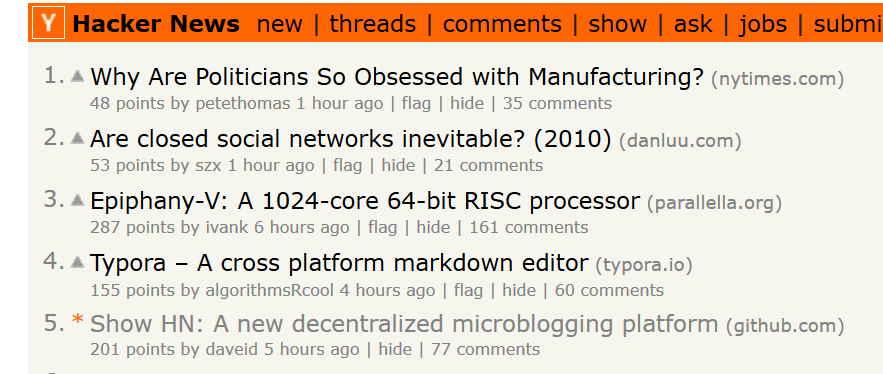
Heh. I misremembered the date--thought it was today, but looks like it was October 5. On that day, 10 years ago, I posted a link to Mastodon on Hacker News, with the title "Show HN: A new decentralized microblogging platform". That it made it to the front page ended up bringing the first 5,000 users, setting the project on the trajectory it's on today.
gabboman the wafrn dev
liked this activity

So, I think my Bluesky is properly linked to my Wafrn account now. 😊


@gabboman there’s a new technique called vibecoding that can help you with that
@akane@masto.es
Wafrn doesnt allow that

多數(다수)의 Hollo 保安(보안) 脆弱點(취약점)에 對(대)한 保安(보안) 업데이트가 릴리스되었으니, 早速히(조속히) 업데이트 바랍니다!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
Holloの複数のセキュリティ脆弱性に対応するセキュリティアップデートがリリースされました。お早めにアップデートしてください!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
A security update has been released to address multiple Hollo security vulnerabilities. Please update as soon as possible!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
多數(다수)의 Hollo 保安(보안) 脆弱點(취약점)에 對(대)한 保安(보안) 업데이트가 릴리스되었으니, 早速히(조속히) 업데이트 바랍니다!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
A security update has been released to address multiple Hollo security vulnerabilities. Please update as soon as possible!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
Matthias Pfefferle
boosted
Das Fediverse ist viel mehr als nur ein weiterer Social-Media-Kanal
Das Fediverse wird noch immer häufig wie ein weiterer Social-Media-Kanal betrachtet. Doch genau das greift zu kurz. Ein paar Gedanken zur Diskussion mit Kai Rüsberg ( @Ruhrnalist) zum #FediLabDay.
kaffeeringe.de
Radio von schräg fotografiert
洪 民憙 (Hong Minhee) :nonbinary:
boosted
Hollo security updates: 0.8.16 and 0.9.24
If you run Hollo, update to 0.8.16 or 0.9.24 now. These releases fix GHSA-v2qh-w789-xxj6, a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use.
For GHSA-v2qh-w789-xxj6, an authenticated client with the write:statuses scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check.
For GHSA-97w4-f4rq-mgqm, Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were 0.8.13 and 0.9.20, incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected.
For GHSA-4qhx-hhwf-8685, Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache.
For GHSA-8863-8468-7hq7, Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually.
Both of these authentication fixes first reached Hollo in 0.8.15 and 0.9.23, incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too.
The other Fedify advisory, GHSA-39gj-rchc-q5m3, concerns Context.routeActivity(): after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in 0.8.14 and 0.9.21. For full technical details on the upstream issues, see the linked advisories and the October 4 Fedify announcement and October 16 Fedify announcement.
The supported Hollo release lines are 0.8.x and 0.9.x under the Hollo security policy. Operators on 0.7.x or earlier should move to a supported line.
For 0.8.x deployments, update to 0.8.16:
docker pull ghcr.io/fedify-dev/hollo:0.8.16For 0.9.x deployments, update to 0.9.24:
docker pull ghcr.io/fedify-dev/hollo:0.9.24After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run docker compose up -d. For source deployments, check out the corresponding release tag, run pnpm install --frozen-lockfile with that tag's pinned pnpm version, run pnpm run build, and restart the server.
If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the 0.9.20 index preparation instructions before starting the new version to avoid blocking writes during its automatic migration.
Thanks to Yami Odymel (@yamiodymel) for reporting the status deletion issue to Hollo, to Adel Zaitri (@adelzaitri) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance.
If anything is unclear, ask below.
gabboman the wafrn dev
boosted
I can now add Wafrn onto the list of places you can find me on! My profile can be found here: https://bark.wolp.chat/blog/WailingQuail
Also linked my Bluesky account to it, hence why my @ changed a little. Now I can have both in one app. 😊

@aria@awawa.club @vriska@lizards.live @sleepybisexual@mk.absturztau.be
 that makes sense
i remembered that post about how they dropped their fairphone in water and it stayed there for a few hours and afterwards only the screen wasnt working (they checked that its otherwise working by screwing the screen from another persons same model phone), and wanted to say  hah iphone sux, but that was in lake iirc, not in pool
@aria@awawa.club @vriska@lizards.live @lystopad@app.wafrn.net @sleepybisexual@mk.absturztau.be
Why’s phone had a battery replacement wich broke water seal thing
