@futurebird Look at the stumulus checks. A few thousand dollars to every eligible citizen cost us BILLIONS of dollars, and drove up both inflation and the deficit. This is no different, except that it's also illegal as it wasn't approved by Congress.
FediDevs
These are the people building the Fediverse!
Thanks for your honest answer Stefano and believe me I'm not bagging them as it seems a great piece of software. It's just the secrecy behind the devs and having no visible git/CVS repo.
@justine The lack of a public Git/CVS repository is their choice, at least for now. They prefer to keep development fairly centralised, partly because there are several branches and some interesting features (!) that aren't ready yet, and they'd rather release them when they're ready.
After all, to me, open source is also about freedom. You don't necessarily have to follow a predefined pattern: announcement, public Git repo, issue tracker, and so on. You're free to manage your project as you see fit.
As I said, I don't agree with every decision, and sometimes I have a hard time convincing them otherwise 😄
But I respect their choices, and I really appreciate their decision to release littleFedi under the MIT license.
And ultimately, littleFedi is out there. Anyone can take the source code, fork it, and continue development in a more "traditional" way if they prefer. That's part of the freedom too. 😄
That said: snac is great - and, unless you badly need something that littleFedi has and snac hasn't, there's no need to migrate from snac to littleFedi.
And if you need the blog...you don't need littleFedi, too, there's BSSG 😉
@coin@fedi.space my main concern is the fan-out that could happen when federating a lot of details across a lot of different places. Federation deliveries go up exponentially when you do stuff like that, and there's still no "story" of how ActivityPub implementations should handle this situation.
Sure, there's some speculative work such as LOLA for ActivityPub data portability, and some platforms like Hubzilla have had some version of this floating around forever. It's that last mile of making it work for everybody that remains hard.
@deadsuperhero@fedizen.net @coin@fedi.space we don't federate those
Kind of a broad #ActivityPub question, for platforms implementing groups in the #Fediverse
We see maybe 2 or 3 different use-cases for how groups are leveraged in the Fediverse today:
- Traditional Discussion Groups: Lemmy-style communities, NodeBB forum categories, basically a moderated Community Actor where people send activities to the group, and the group actor relays them to all group members.
- Publication Groups: WordPress-style, the Group Actor represents a publication, and individual Actors serve as the article authors.
- Structured Account Groups: PeerTube-style, the Account Actor is the parent object that delegates everything for Child Actors representing individual channels owned by that account.
So, I guess my question is: let's say your instance has an index of known remote groups. You just want to show discussion groups, not PeerTube accounts or Flipboard collections. How do you denote the discussion groups, and filter out the rest?
I really need otherwise sensible people to stop treating complexity as inherently scary.
Ulrich Rozier
@javascript stolas so baby
@ana_r@todon.eu
Y loona…
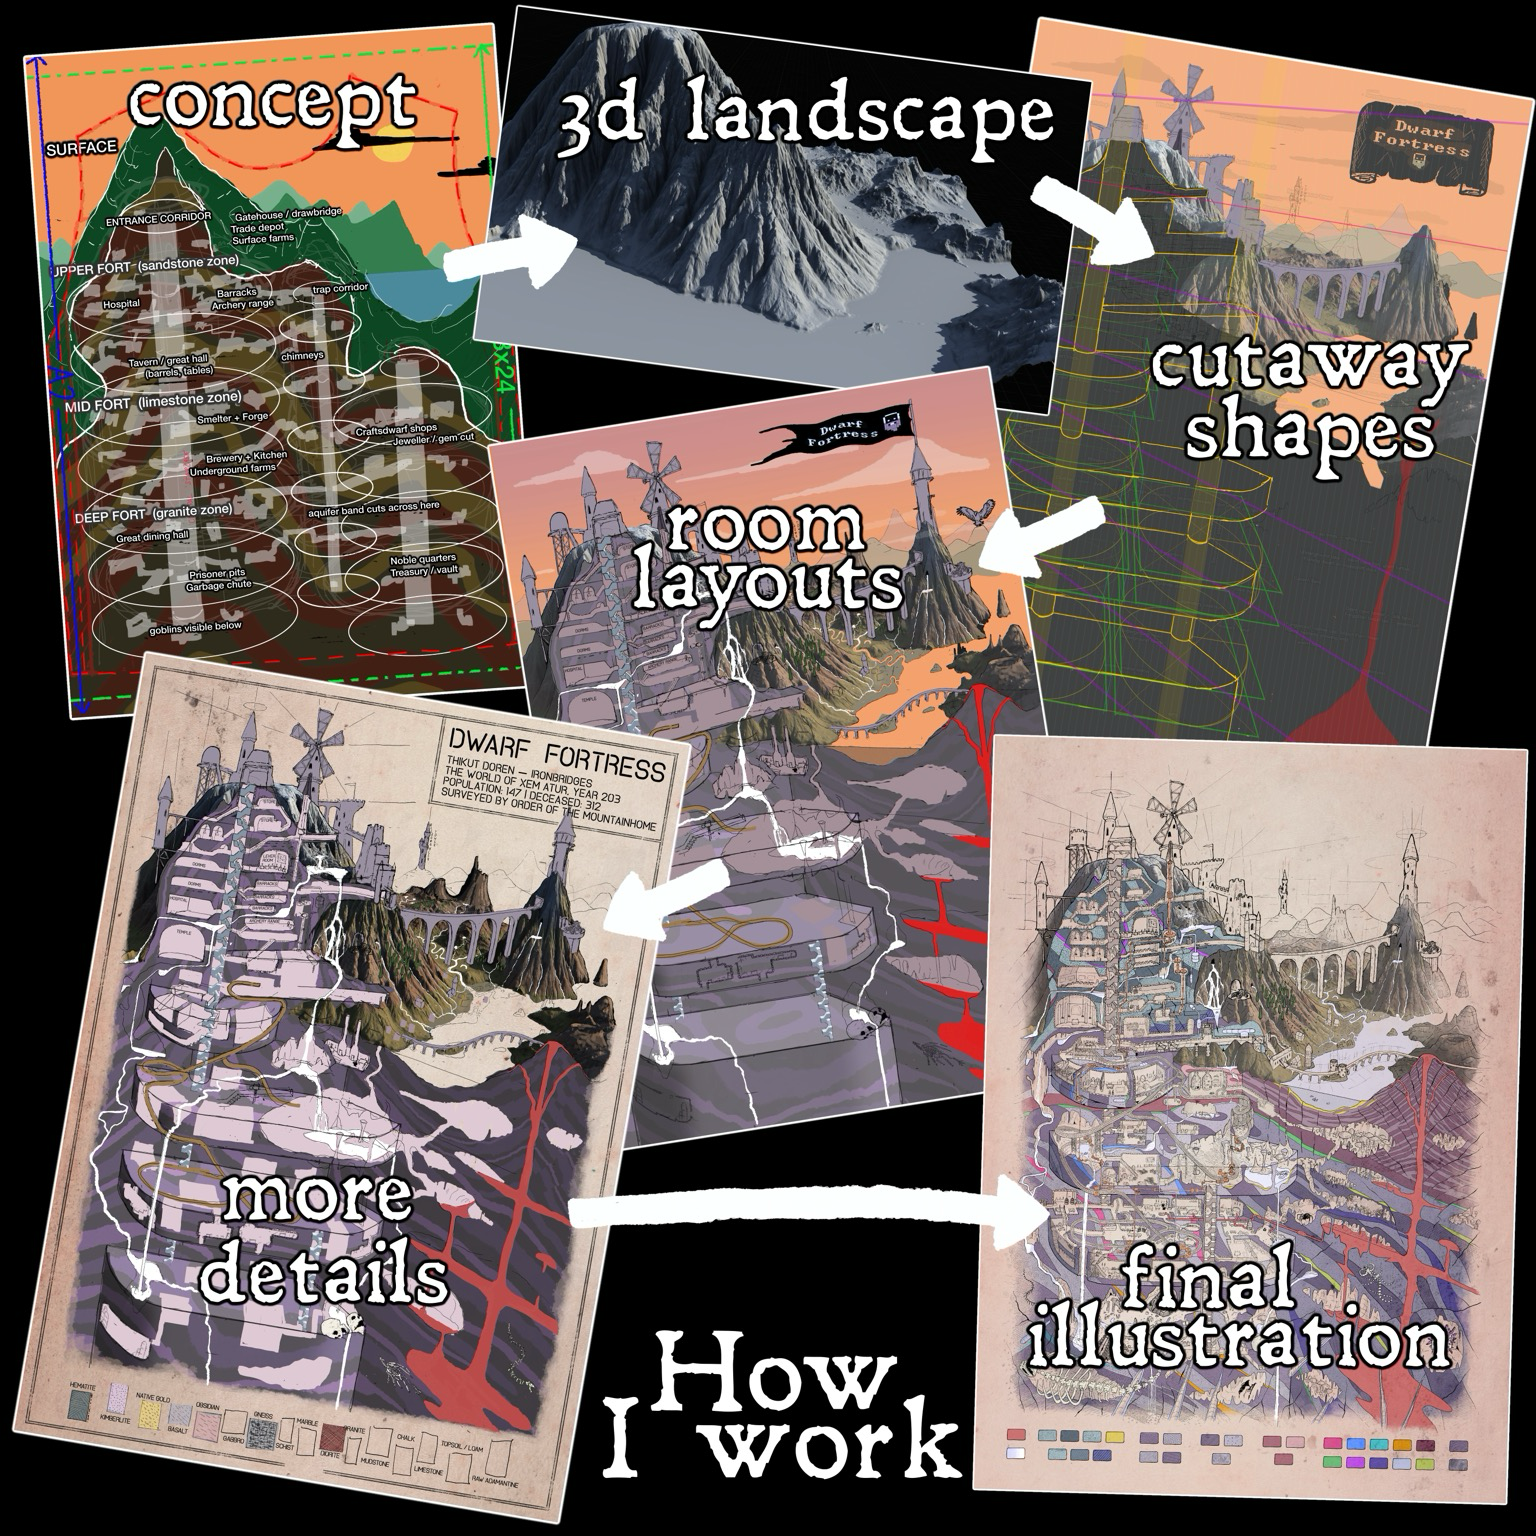
The dwarf fortress map also made use of Gaea for the above ground landscape, with me adding all the other details on top. Working out how power, water, mine carts, stairs and lava tubes all connected was a lot of fun. #map #cartographer #dwarffortress #cutaway #cavemapping
So I'm testing #LittleFedi and it does seem really good but this one thing keeps praying on my mind. Why would the group of people that make it want to remain anonymous? Is it because if folk found out and linked them to something that happened in the past which they'd rather avoid? Or am I just over thinking this maybe? I do like it but I love #Snac too and it is my first love. What's everyone else's thoughts on the secrecy behind LittleFedi and it's overall usability over other software out there like Snac, GTS and Mastodon ?
@justine There are various reasons. I agree with some of them, but not with others. On the other hand, many projects have developers who are known only by their nicknames, so they're effectively anonymous anyway.
And yes, at the heart of it are some bad experiences (from a few years ago) that led them to take a step back from putting themselves out there on social media.
Or maybe they're still around, and we just don't know it? 😉
@javascript stolas so baby
If you actually read the “Passkeys are a trap. Do not use them.” post going around, you’ll find a transparent attempt to clumsily string together a conspiracy.
The post is predicated on the idea that a feature of WebAuthn called “attestation”, which is only used in high-assurance and usually corporate scenarios, and usually with physical hardware security keys, will be leveraged to hurt people, somehow.
The post posits that a website like X will bait and switch users: first, you get a passkey. Then, later, scary “attested” passkeys! This simply isn’t possible to do because attestation isn’t supported on the web for mass market, consumer authentication.
Attestation for passkeys (software-based, syncable credentials) is antithetical to their mass market goals, and would freeze out independent, non-corporate-backed credential managers. It’s an explicit non-goal of the designers of passkeys, who work together in a forum anyone can join.
And trust me, websites and apps like banks repeatedly asked for attestation at the beginning of the industry’s passkey journey. The platforms, browsers, and credential management apps have held firm that the goal of passkeys is reducing phishing and **not** some kind of trusted computing scheme. (And I will note: over my dead body!)
Besides the theory of the case being fundamentally wrong, there are several things that make the post disqualifying in terms of arguing something useful or important in the realm of security, privacy, and user authentication:
1. Intentionally presenting things that are complicated as inherently suspicious. (Delivering security by design can be complicated, yes!)
2. Describing TOTP as a “great solution” for adding security to a password-based account. When the most common threat model on the web is phishing (a word the post never mentions!), TOTP hardly buys you _anything_. TOTP is phishable.
3. Seeming to be unbothered by how many logical leaps are being taken without actually understanding the topic being discussed.
There are bad things happening in tech and untrustworthy people and companies do exist, but they’re largely in the AI space, not the “let’s stop people we love from getting compromised through phishing” space.
“Daddy, what is class inheritance?”
The perpetuation of class distinctions and oppression through bloodlines over generations. Avoid it.
“I meant in programming?”
Avoid that too.
Les bras m'en tombent (vraiment cette fois 😉 : 100 000 vues en -de 24h pour une chronique linguistique sur les défigements, je n'aurais jamais cru ça quand j'ai lu pour la 1ère fois Benveniste! 😂C'est la magie de "La Dernière" @laRadioNova https://www.youtube.com/watch?v=JirnZB9lQdY&t=5s
“Bardella antisémite? Qui l’eût cuit?” Les défigements - La chronique de Laélia Véron
YouTube
RE: https://mastodon.social/@Gargron/117424047946230444
Hey other #NoAI fans, the replies in this thread make it very easy to block, so go and block away! But thank you for making this block honney pot!
RE: https://mastodon.social/@Gargron/117424047946230444
Hey other #NoAI fans, the replies in this thread make it very easy to block, so go and block away! But thank you for making this block honney pot!
@WeirdWriter Happy to be of service!
@MastodonEngineering A question about followers only posts and the window of visibility.
Bear with me as I lay out the scenario:
1. I recently sent a post to followers only.
2. A follower replied
3. A non-follower replied to the reply
4. Non-follower sent a friend request, which I approved
5. Former non-follower was able to Like the original post.
My question is about how the former-non-follower was able to see the post.
Was it because there is some window of access?
Because I have a follower on the same server as them and their new follower status somehow allows them to see it?
Or, because the post hadn’t yet been sent to my followers on the same server, so that when it was sent they were included?
Or some other explanation!
I’m very curious as this broke my previous understanding of mastodons federation and visibility model.
I got a call from someone I don't know.
"Hi. We have a FreeBSD server. It's been working perfectly for years, but it hasn't been updated since then. We asked AI to update it, but now it won't boot anymore. It didn't even make a backup before starting. The AI keeps trying things, everything is down, and we've already spent over €500 in tokens. Can you help us?"
"Sure. €500, plus the time it'll take me to try to fix it. Assuming it can still be fixed and nothing important has been deleted."
"That much?"
Some silence.
"Well, I hope AI takes your job away!" And he hung up.
Believing that autopilot automatically makes you an invulnerable professional pilot will ruin far more people than job losses will.
I don't know if AI will take my job away, but it's already cost them €500 and, probably, their server.
En lo que llevamos de mes nos hemos acabado hazbin hotel, helluva boss, over the garden wall y los soprano, la que más me ha gustado ha sido over the garden wall pero la que tengo ganas de volver a verme ya es helluva boss. Mira ue cuando la empecé pensaba que me iba a gustar menos que hazbin pero soy una sucker de las tramas que en principio no parece que vayan a ser románticas pero resulta que sí
@ana_r@todon.eu
Es que helluvaboss es un seriote
On ne change pas des opinions matrixées depuis des années par une ou deux conversations.
C'est normal de se sentir impuissante ou impuissant dans ce genre de configuration.
C'est un travail de fond sur les plans de l'éducation, du dialogue et de la décentration, et sur les conditions de (sur)vie de chacune et chacun.
La route est longue.

My partner: “this tool doesn’t involve AI does it?”
Me: “oh heck no, at least not the modern definition you mean. It’s a tool called lazy clause generators…”
I’ll use llms help me build the thing, but I’m not about to stick them in the actual decision chain here. The last thing we need is it forgetting a content warning or somesuch