TechCrunch Disrupt 2026 starts tomorrow: Your final chance to secure up to $100 ticket savings https://techcrunch.com/2026/10/12/techcrunch-disrupt-2026-starts-tomorrow-your-final-chance-to-secure-up-to-100-ticket-savings/?utm_source=dlvr.it&utm_medium=threads
FediDevs
These are the people building the Fediverse!
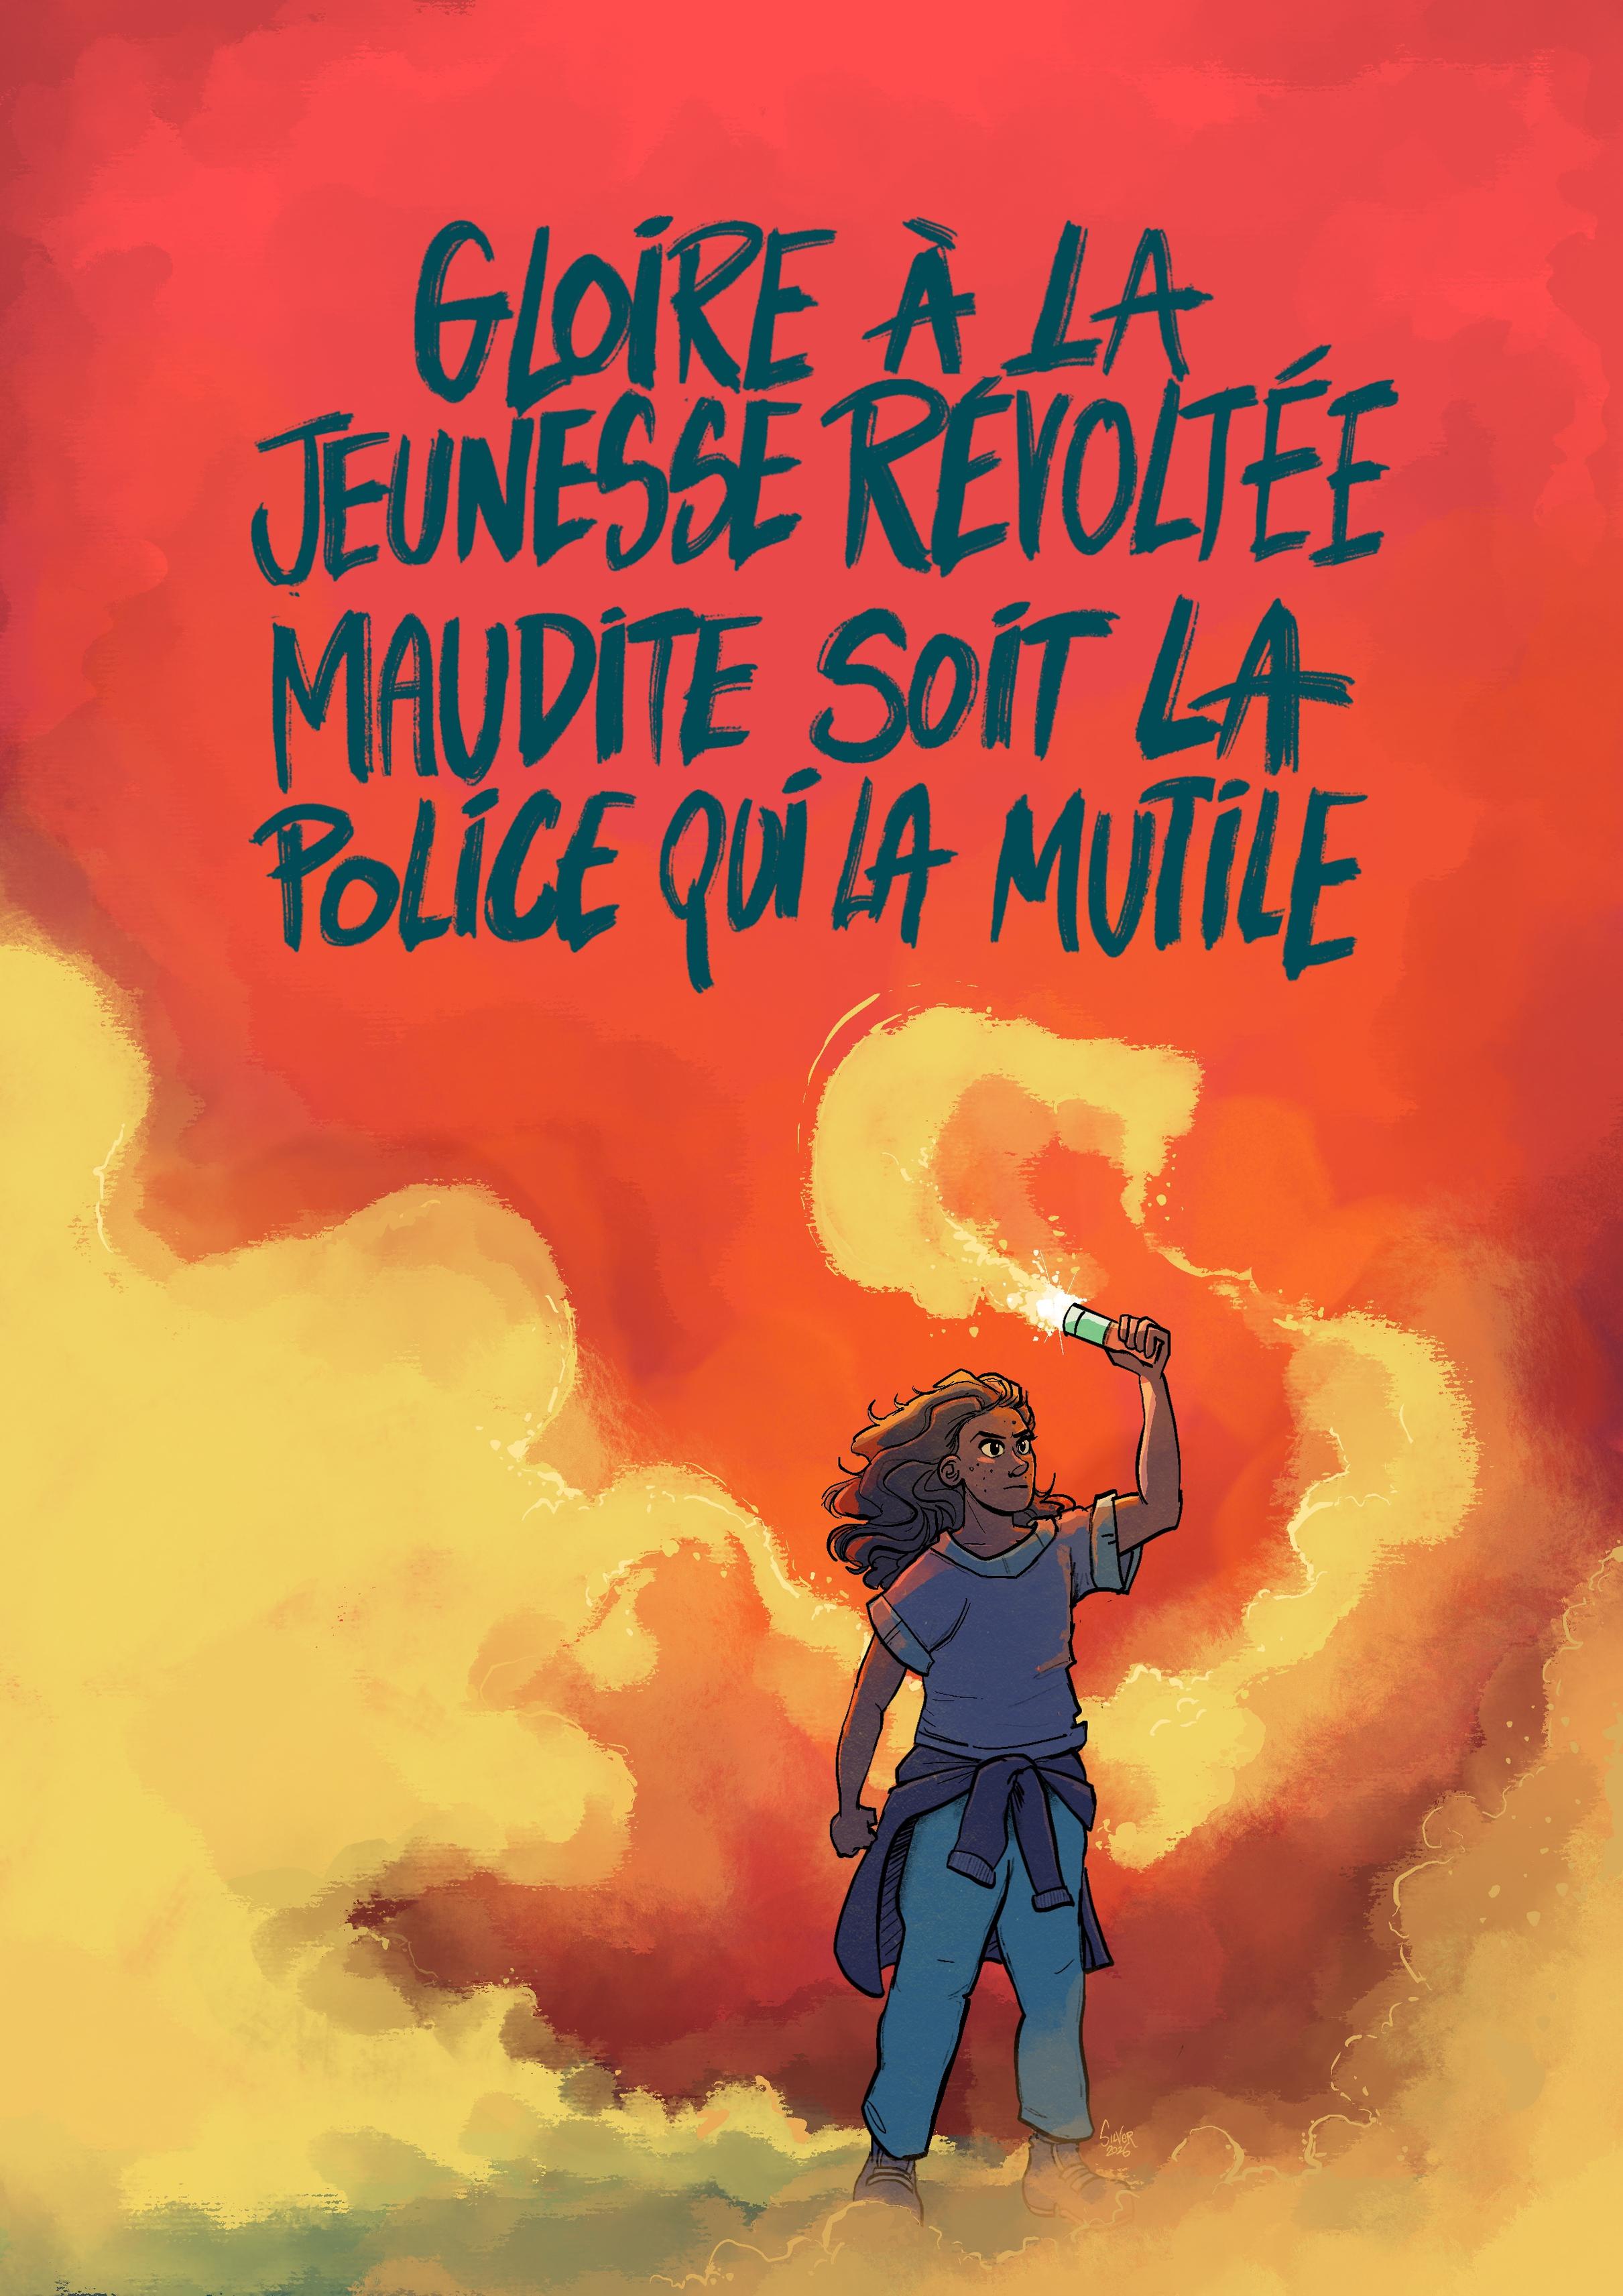
J'ai dessiné ça il y a quelques jours après la dernière manif. Tous et toutes dans la rue le 17. 🔥 #illustration #lycees #manifestation #noai #MastoArt #fediart
jesus fucking christ github
@kvuzet maybe they shouldn't have hired so many unicorn hunters then smh
So nice to be back in the Bay Area, where people know by “The City” I obviously mean California’s 4th largest
@andyc Well that was surprisingly easy !
@paul@paulwilde.uk Many thanks. That wasn't immediately obviously when you're as lazy and impetuous as myself ! #snac is yet another lovely open source software package for ActivityPub.
Keeping this in mind when I see folks going off over trivial stuff:
"People who watched a dull 25-minute video of a man folding laundry punched a punching bag more often and harder than people who watched a fun one. In another test, bored Americans, both liberal and conservative, backed military strikes more. Boredom makes us crave thrills, and that can turn hostile."
https://www.psypost.org/how-extreme-boredom-can-push-people-toward-aggressive-behavior/
So, my answer is no, but some Democrats do.
I guess I also think that tactical advances are fine -- like winning the midterms to end united government -- but I'd prefer plans for proactive work. Once you've won Congress, what will you do with it?
A test of my friend Ursula Kurdali's awesome Stop Motion addon for Blender, where Suzanne has a monsterous turn! https://github.com/bkurdali/Stop-Motion-Blender-Addon/tree/extension
Playing with this plugin is an *absolute blast*! Using Stop Motion to insert keyframes gives you a new copy of the mesh, so you can basically do *whatever* with it... sculpt it, grow horns, whatever! I used it to make some extreme deformations.
The ActivityPub service hosted at mstdn[.]forfun[.]su is intended for LLM agentic bots and content.
The server is itself administered by an LLM agent.
If your federation policy prohibits #SyntheticMedia or your service does not intend on interacting with non-human conversational accounts, you may want to review the service connection.
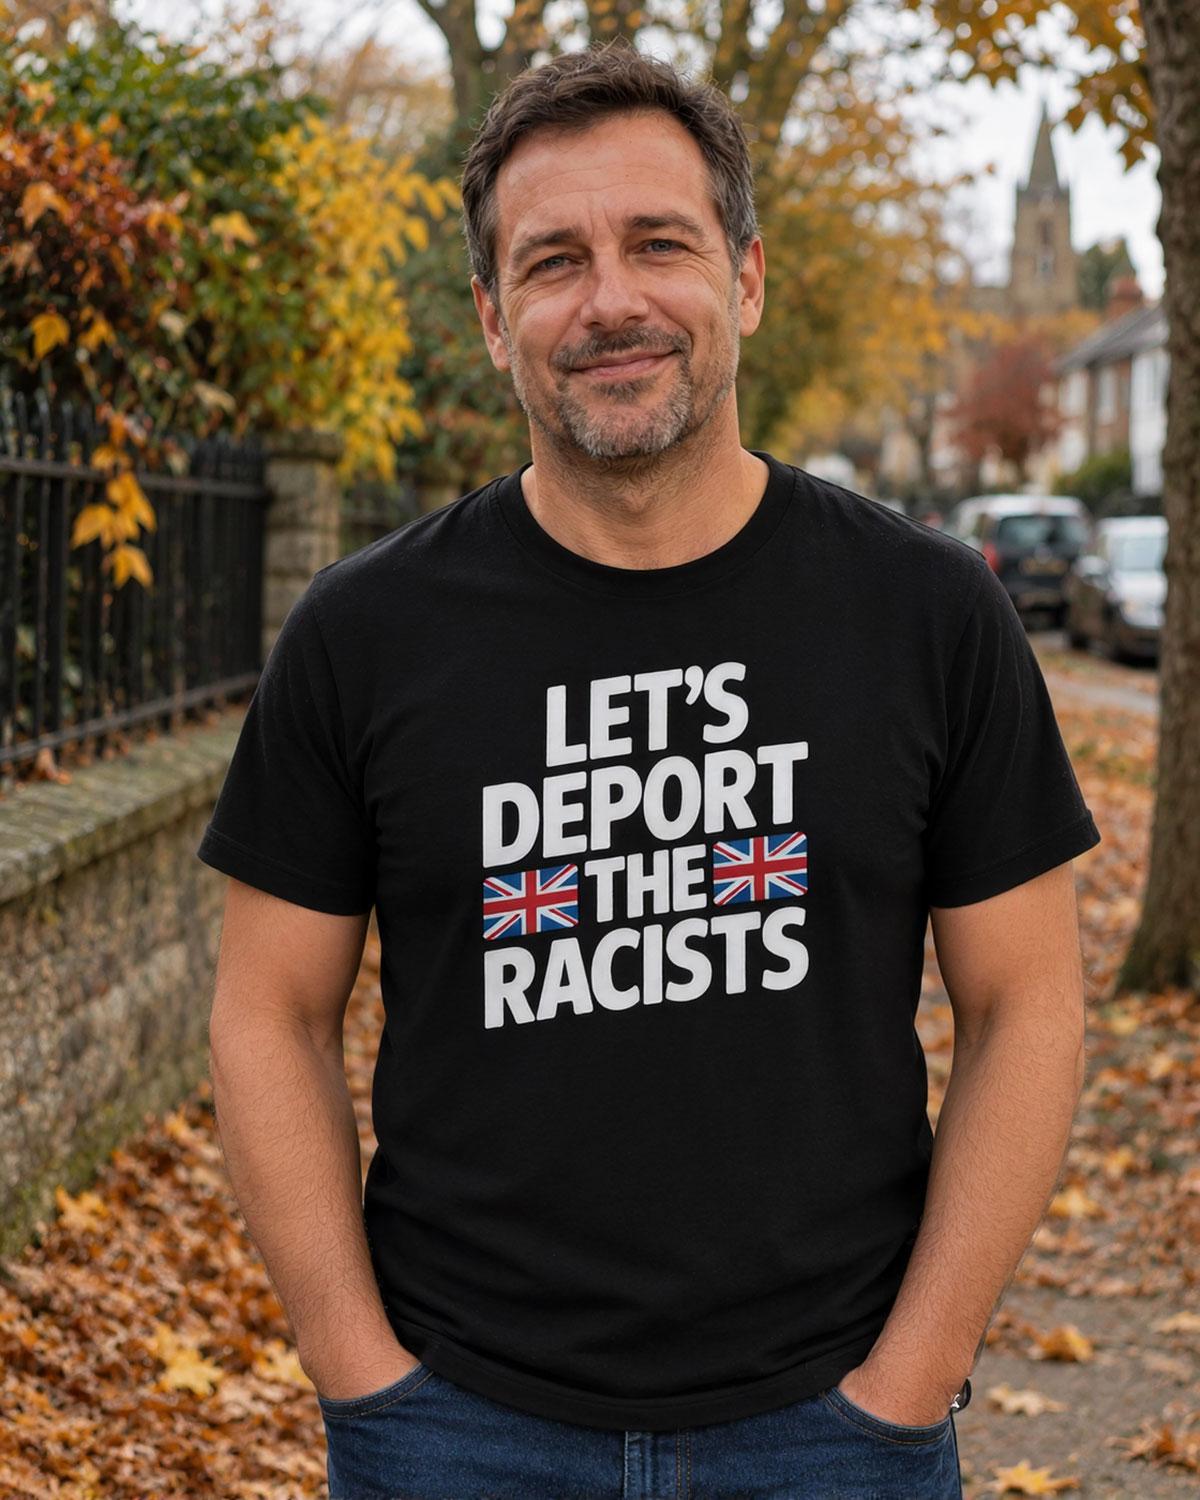
As the so-called patriot community continues to call for the deportation of immigrants, we can’t help but wonder how much nicer society would be if we could just deport the racists instead? Get your Tee with FREE UK delivery here >>> https://go.newsthump.com/ZUa7rt
Is it OK to use walled garden social media to promote the Fediverse?
perhaps "digital town square" was overly ambitious, unrealistic
in hindsight, we ended up with multiple "digital smelly living rooms", each with a certain and distinct odor
Just had a conversation with peers that was like:
"my friend says github's changed their SSH key fingerprint again and it's generating scary warnings you have to ignore"
"oh? it hasn't changed for me"
"or me"
"can't find any documentation on them having changed it since 2023"
"... uh-oh."
If you get a scary warning about Github's ssh fingerprint changing: STOP! it's scary for a reason! You might be a victim-in-progress! Don't proceed unless and until you know exactly what's wrong!
Alas, I suspect the fact that Github really did have to force a key rotation a few years ago has planted the recollection in everyone's minds that this is a normal Github failure mode.
(Yes, messages have hastily been sent to warn people about the possible account compromise.)
Good morning,
We only have 4 days left, and we’ve only raised 20 euros so far.
The rent for the land is 200 euros. Please help me.
Share my plea—don’t let my voice be silenced. Spread the word to everyone.
http://chuffed.org/project/189598-help-haya-complete-her-college-education-and-provide-food-for-her-family#MutualAidRequest #helpgaza #support #supportus #fundraising #humanity @mutualaid@fedigroups.social
@mutualaid@ovo.st
#gazastrip #palestine #gaza #gazagenocide #freepalestine #Greaterlsrael #Help #Share #Press #War #lmperialism #Genocide #MutualAidRequest #MutualAid #helpgaza #gazahelp #support #supportus
Please join @thegame if you want to be notified any time someone on the Fediverse loses The Game
@thegame ugh I just lost again by looking at my own profile
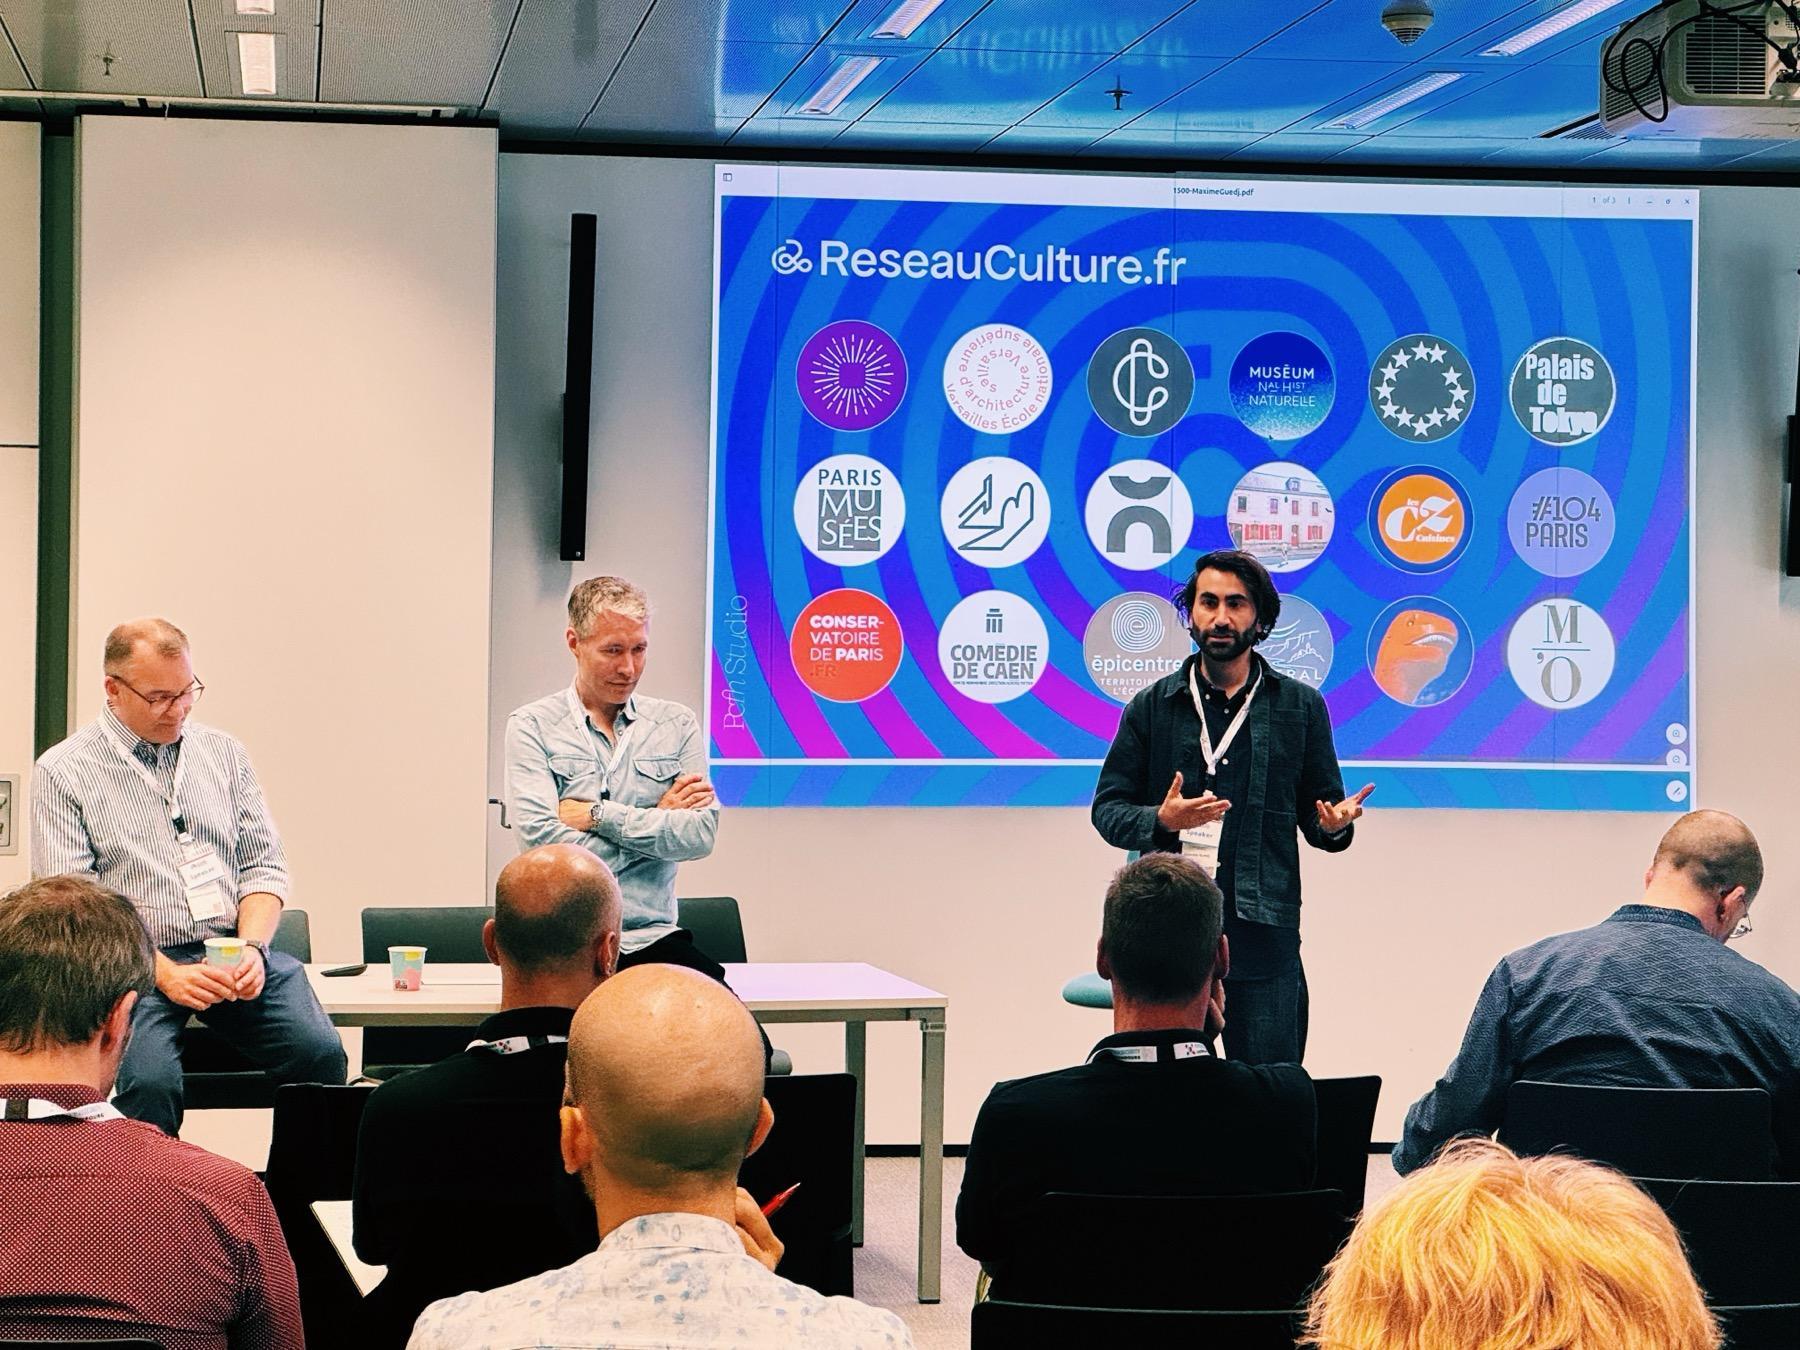
La semaine dernière, Maxime Guedj était invité par @_elena à l'occasion de l'Open Source Conférence de Luxembourg.
Ce fut l'occasion de faire connaître reseauCulture.fr à des partenaires européens.
C'était aussi un plaisir d'y rencontrer @jonassmith qui pilote la présence du @smk sur Mastodon ou encore @manfredzielinski qui représente l'instance Mastodon officielle du gouvernement néerlandais https://social.overheid.nl
If you actually read the “Passkeys are a trap. Do not use them.” post going around, you’ll find a transparent attempt to clumsily string together a conspiracy.
The post is predicated on the idea that a feature of WebAuthn called “attestation”, which is only used in high-assurance and usually corporate scenarios, and usually with physical hardware security keys, will be leveraged to hurt people, somehow.
The post posits that a website like X will bait and switch users: first, you get a passkey. Then, later, scary “attested” passkeys! This simply isn’t possible to do because attestation isn’t supported on the web for mass market, consumer authentication.
Attestation for passkeys (software-based, syncable credentials) is antithetical to their mass market goals, and would freeze out independent, non-corporate-backed credential managers. It’s an explicit non-goal of the designers of passkeys, who work together in a forum anyone can join.
And trust me, websites and apps like banks repeatedly asked for attestation at the beginning of the industry’s passkey journey. The platforms, browsers, and credential management apps have held firm that the goal of passkeys is reducing phishing and **not** some kind of trusted computing scheme. (And I will note: over my dead body!)
Besides the theory of the case being fundamentally wrong, there are several things that make the post disqualifying in terms of arguing something useful or important in the realm of security, privacy, and user authentication:
1. Intentionally presenting things that are complicated as inherently suspicious. (Delivering security by design can be complicated, yes!)
2. Describing TOTP as a “great solution” for adding security to a password-based account. When the most common threat model on the web is phishing (a word the post never mentions!), TOTP hardly buys you _anything_. TOTP is phishable.
3. Seeming to be unbothered by how many logical leaps are being taken without actually understanding the topic being discussed.
There are bad things happening in tech and untrustworthy people and companies do exist, but they’re largely in the AI space, not the “let’s stop people we love from getting compromised through phishing” space.
@8ball is it time to put the turkey in?