
security guidelines for 2026:
DO NOT RUN ANY TYPE OF SERVER ACCESSIBLE TO ANY TYPE OF NETWORK ACCESS
security guidelines for 2026:
DO NOT RUN ANY TYPE OF SERVER ACCESSIBLE TO ANY TYPE OF NETWORK ACCESS
@foone ah the 1992 security guideline is in full effect again
@foone and even on offline devices, don't forget to disable terminals!
and watch out for boot sector viruses on any floppy disks you insert
CLIENTS ARE ALSO ON THIN FUCKING ICE
my new plan for a secure website in 2027 is that I'm gonna host my wiki as a static HTML site on a windows 95 VM that gets reset after every HTTP request
@foone Too hackable. Burn the whole website on to EPROM and have a 7400 series logic state machine handle the TCP connection and barf out the EPROM contents.
@foone This could be relevant to your interests: https://github.com/mirage/mirage-skeleton/tree/main/applications/static_website_tls
Basically put the kernel, app, and static payload files into on binary and boot on a VM.
@foone my personal plan is to draw on paper the page and send the drawing via postal service upon page request received via postal service.
@foone lol I genuinely have a preference for HTML static sites for maximum security. I never worry about stuff. Let's go back to 90s website pls.
@foone Unfortunately cracking the Windows 95 could easily lead to privilege escalation out of the VM.
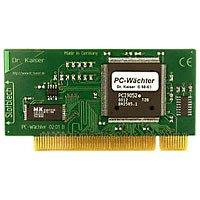
@foone just get one of these bad boys and reboot once in a while 😅. We had this all solved pre Windows NT.
Those really worked wonders, if you didn't forget to disable them before you made your administrative changes.
I wonder how they actually work, but I think they're low level hooking some HDD interrupts/routines and just hide half the disk to keep the clean copy. (Never really looked into it while I was using them back in the early 2000s)
@foone You jest, but I'm seriously working on a script to capture a wiki using httrack, process using perl (instead of sed for better regex support) to remove login links and the like, and pushing that as the public version of a website using rsync.
The "editors" would then use a private site to make edits, and a cron script would send updates (or be manually pushed)
@foone Serve printed pages over postal service. And even then I’d remain paranoid.
Packets may be transmitted via carrier pigeon or via lore, passed down through the generations around the fire.
Do the boot sector viruses have a valid Secure Boot signature?
@foone when in doubt - EMP out!
@foone this includes electrical networks, build your own voltage regulator and connect to solar panels.
@foone "DO NOT", got it
@foone A worthy successor to "DO NOT RUN WITH SCISSORS". When will we be seeing it in the MS Word splash screen?
@foone the more things change...
@otaku the only thing that keeps me from having that dream is that I grew up in the woods. I spent my first decade living in a big house in rural north carolina on 35 acres of forest, and I dreamed of running away to computers
@foone Per PLC (powerline communications), comptrons may only be powered by batteries
@foone sounds like the 1990s advice that your windows box is secure provided you bury it in a metre of concrete
@foone Maybe shutdown the Internet altogether? ;-)
@foone
🎶 Turn off your computer and make sure it powers down
Drop it in a 43-foot hole in the ground
Bury it completely, rocks and boulders should be fine
– Weird Al Yankovic, "Virus Alert"
https://youtu.be/zvfD5rnkTws
YouTube


















@foone setting up a PO box where people write http* requests on postcards and i mail the responses back
* http >1.1 not supported