

🗝️ Any passwords over 256 characters are fine.
Ref: https://sshhole.com/
9 Boosts
1 Like

@davidrevoy there’s also an explanation w/o Avian Intelligence https://www.alpinelinux.org/posts/2026-11-05-openssh-password-authentication-bypass/ (h/t https://infosec.exchange/@nothacking/117565320398045332)


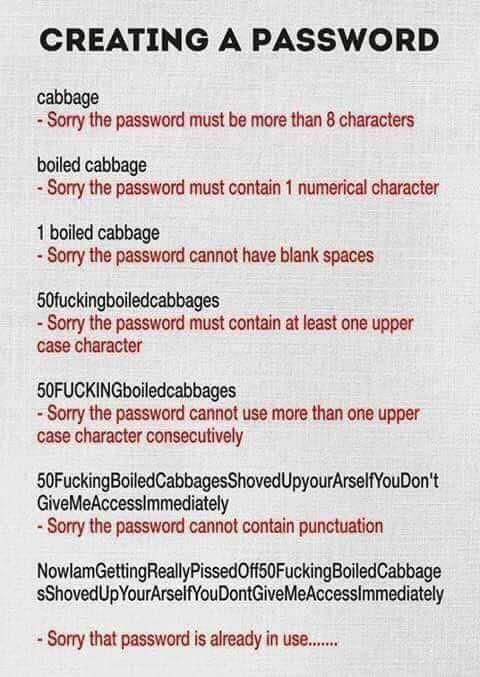
@davidrevoy I never liked the ‘*’ character, it always seemed to me that it was used too often in places where something else would be more appropriate and that it didn’t deserve to be one of the few symbols which are compatible with legacy systems. Who would guess that the evil asterisk would go this far?


@davidrevoy My first guess would have been "4."

@davidrevoy but pls, make it a nice shortstory!
As a millionaire living my best life, I'm giving $20k to the first 5 people who message me"GRACE" | understand that many people are struggling with bills, and I want to help reduce that burden


Yet another reason to disable password authentication entirely. Key or GTFO.


@davidrevoy I absolutely love, that a real human artist made it a meme/comic, before an AI slopped it! 💚


@davidrevoy did anyone else read that password in goat? 🤪
@davidrevoy
> oh did i say "i"? sorry. i had agent swarms. a lot of them. let's not get into it
genai agents instead of a series of `for` loops?
Colour me annoyed.
@dzwiedziu True. A bash script of 500 lines could have tested and found this one for probably 0.01% of the computational costs...


@davidrevoy AAAAA.....AAAAA\x33\xc0\xff\xd0

@davidrevoy Do I have to disable password-login for the user ('*') to enable this? Couldn't reproduce on some older OpenWRT boxes. 🤔