
oh this looks nasty
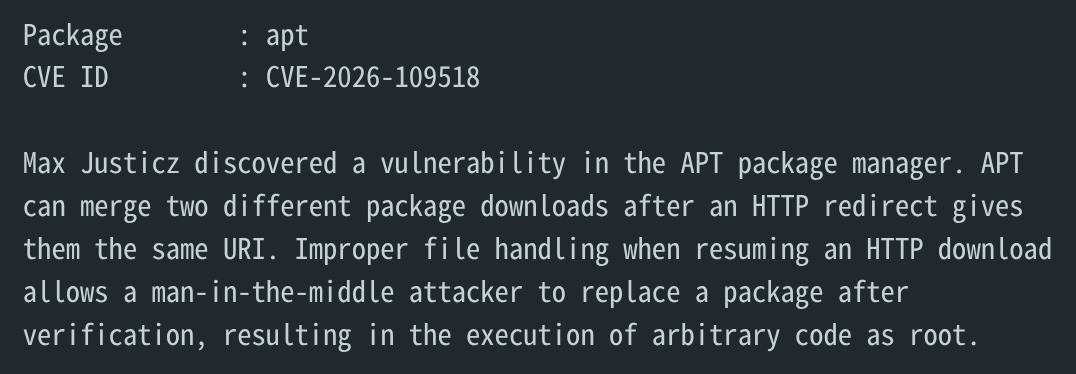
1 Boost
0 Likes

@whitequark This... only helps if there's a signature match on the result? Or?
Edit: oh, after verif... whaaaaat.
@whitequark wait what in pickles is getting verified if it's verified before it's downloaded
This federated comment is not yet available here.

@lizbian @whitequark yiiiiiikes. In 2026? Really?
@ratsnakegames @lizbian when serving static content it's easy to get in a situation where TLS is your bottleneck so I don't think this is outrageous, but yeah it's not great in this particular instance
@whitequark @lizbian i mean, i get that the certificate system built into apt is supposed to protect against MITM so HTTPS isn't strictly speaking necessary for that purpose, but after Snowden i'd have expected HTTPS to be enabled for privacy alone
@ratsnakegames @lizbian discussion as old as time https://web.archive.org/web/20190620135309/https://whydoesaptnotusehttps.com/

@whitequark does apt use HTTP per default rather than HTTPS? I reckon HTTPS would largely mitigate this
@d_rift @whitequark i did do an update in the several weeks since that dropped and i suspect so has every other responsible sysadmin

@whitequark source: https://lists.debian.org/debian-security-announce/2026/msg00526.html
Somehow it's not listed on the Debian security tracker yet. https://security-tracker.debian.org/tracker/source-package/apt
Information on source package apt
[SECURITY] [DSA 6607-1] apt security update