Used to hang out with Erica in IRC back in the day. Glad she's doing well. Fuck your coordinated disclosure
0 Boosts
0 Likes


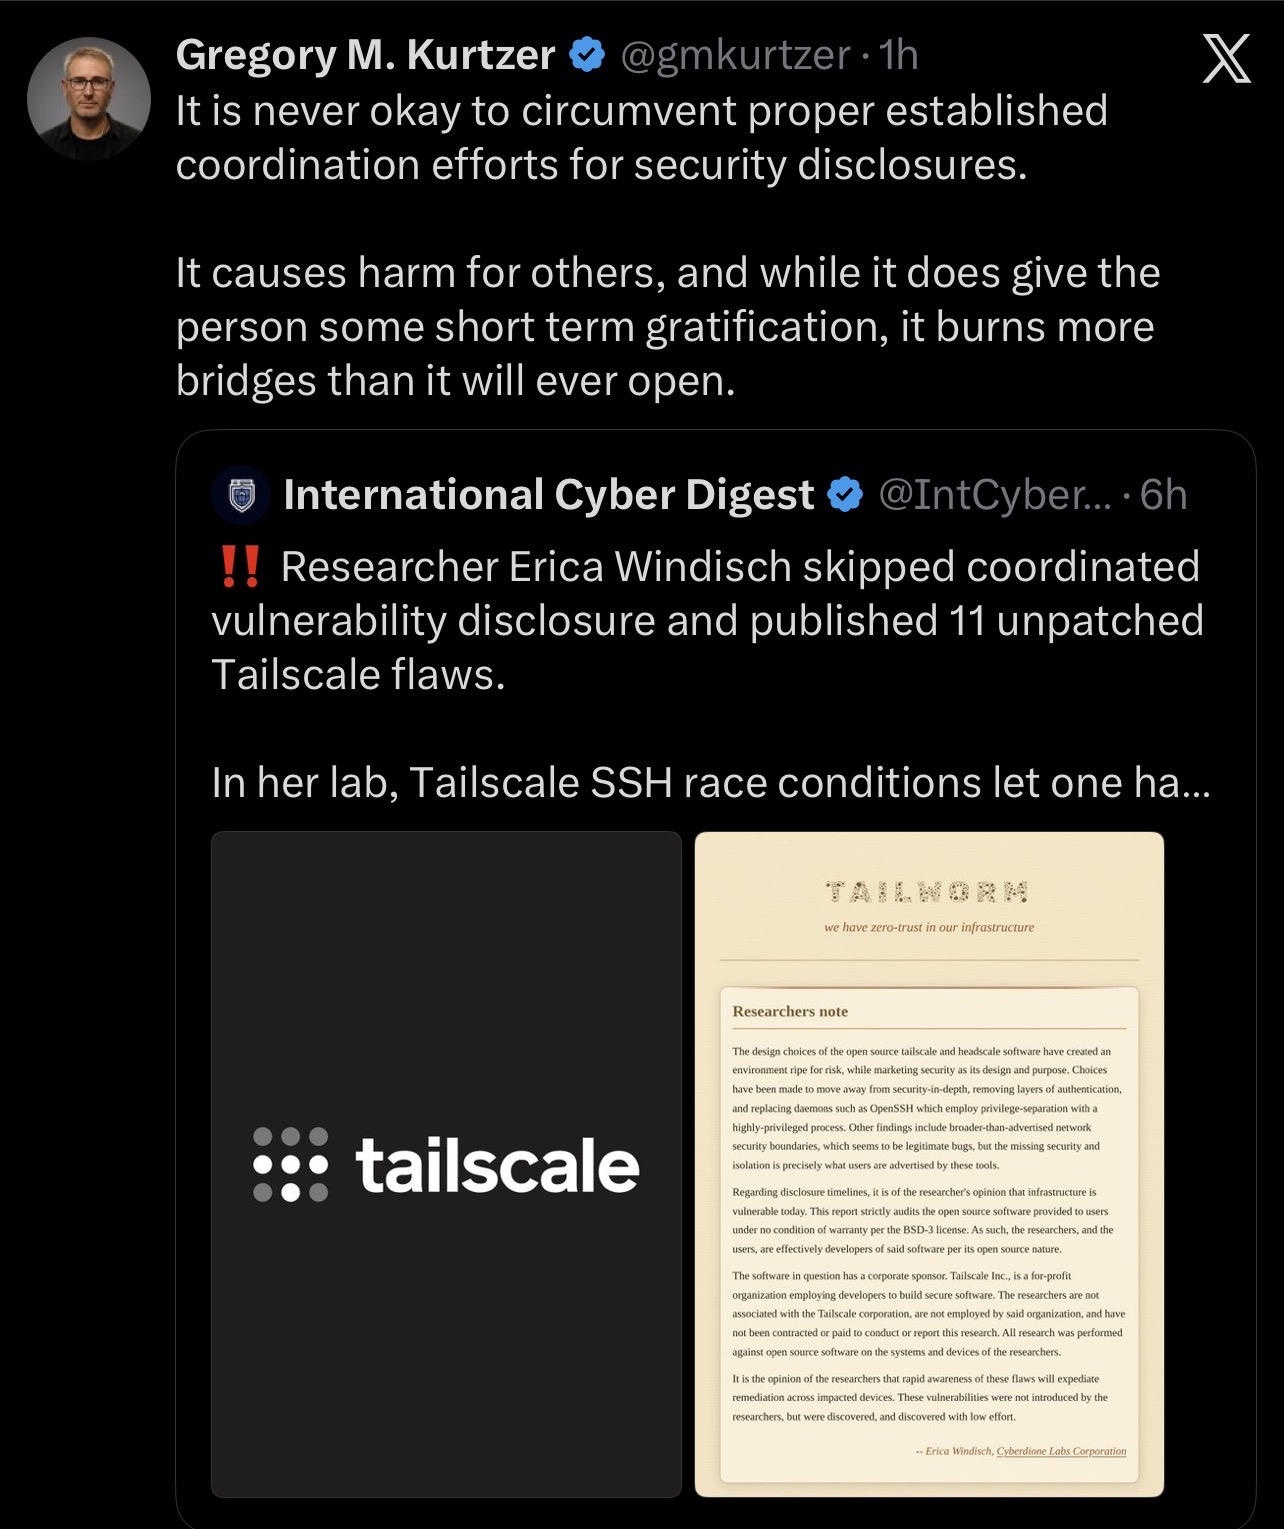
@feld wait, circumventing coordinated disclosure seems only ok if sufficient notice is given otherwise if you’re just publishing it without caring, you’re being the asshole, no? What are the details here? Did they sit on the notice for too long and ignored it?
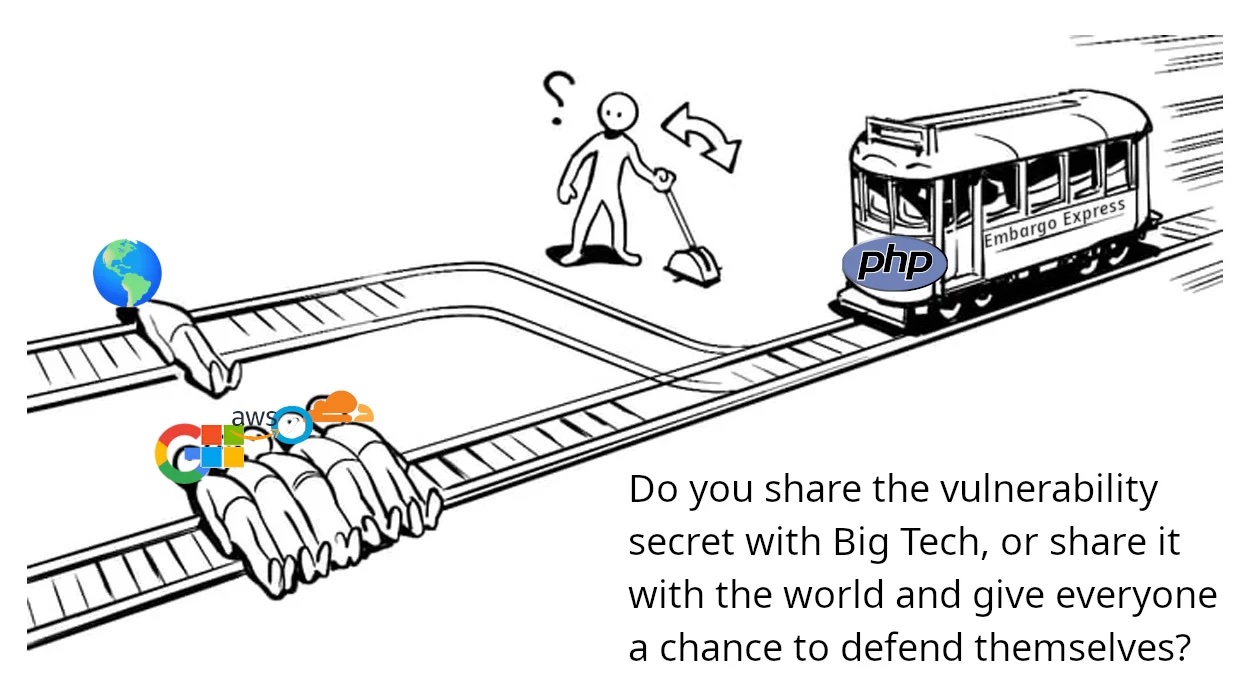
@990000 Coordinated / responsible disclosure exists to protect the wrong people from consequences. It lets companies and corps protect themselves and leaves everyone else like small businesses waiting until the last second to find out there's something to address which means as soon as it goes public they're the ones most likely to be viable targets of attacks because they didn't have time to process the information, audit their infra, and plan their patches. Sometimes the people with embargo details actually get the patch in secret as well
@feld I think we’d need actual details of this incident, not conceptual/philosophical explanations.
For example, how can it be right to blast the entire web with a disclosure which includes bad actors without giving the maintainers of code a chance to fix things first? Like, if I were using a service with a vulnerability, I’d prefer to have them at least patch their end of things before I need to patch mine.
I don’t think I have enough information about this.
@990000 The maintainers can't always be trusted to be the good guys either. Like I said in another post, what happens if one of the devs is a Russian sympathizer and leaks the details to someone connected to the GRU so they can use it against Ukraine during the embargo period? And maybe they extend the wait before patching so attack campaigns can continue in secret? All entirely possible
None of this process really works the way we imagine. The guy who leaked the PHP details claims two people before him were never told there was an embargo. Person X told Y told Z who then posted the details on HackerNews and everyone in that chain claims to have no knowledge an embargo existed
None of this process really works the way we imagine. The guy who leaked the PHP details claims two people before him were never told there was an embargo. Person X told Y told Z who then posted the details on HackerNews and everyone in that chain claims to have no knowledge an embargo existed


@feld LOL private disclosure is a courtesy, not a privilege

@feld
Bug picture, as a layman "coordinated disclosure is the only responsible option" seems like a convenient lie for the sake of protecting institutions/groups at the expense of people.
The public has no stakeholders or representation (in most cases) so offsetting risk and harm is the logical choice for "industry standard"...
@gabriel Yeah it's for protecting the economy and we should stop doing that for free. It's not our responsibility when the corps and govs aren't investing in this critical infrastructure.

@feld yeah, tailscale.com/security explicitly says they don't have a bounty program, but still expect certain behaviours from others. Sorry, but I'm definitely not going to jump through your arbitrary bullshit hoops if you, as a commercial entity who will gain economic benefit from my work, aren't even going to compensate me for the hoop jumping.