
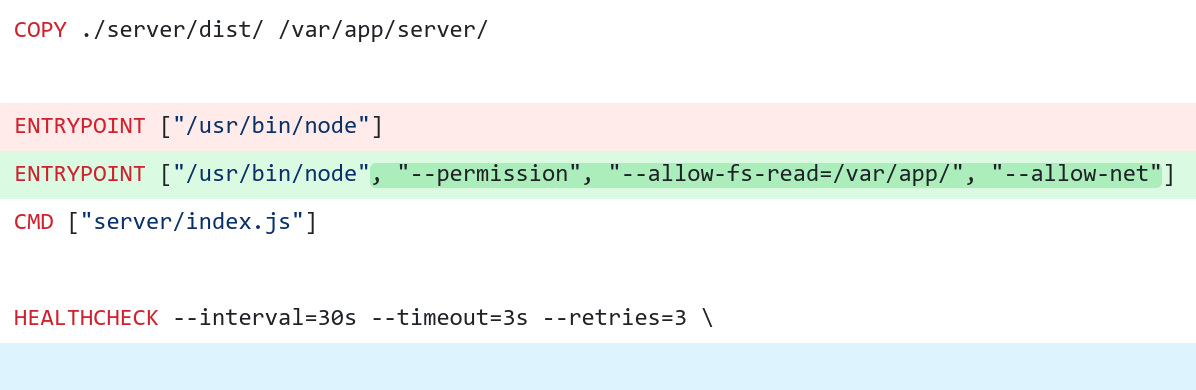
If you run a Node.js server, start it with --permission and grant only what it needs:
— No network access if it only reads files
— Limit file access to the directories it actually uses
Here's how I locked down Slow Reader's server:
https://github.com/hplush/slowreader/commit/25b5730374eefd2591a8729efe219c5d64534277

@sitnik_en It's a bit misleading to call Node's permission model a sandbox. The documentation explicitly says that "it does not provide security guarantees in the presence of malicious code".